Web Application Penetration Testing
Manual web application penetration testing for authentication, authorization, business logic, injection, server-side, and browser security flaws.
FREELANCE SECURITY · MANUAL PENTESTING · ATTACK SURFACE
Freelance penetration testing across applications, APIs, infrastructure, cloud, mobile, AI systems, and product security workflows - with clear evidence your developers can act on.
TELL US ABOUT YOUR SCOPE
Share a few details about the target and your goals. We will reply with the right testing approach and a clear proposal.
Protected against automated submissions. Only submit systems you own or are authorized to test. Do not include passwords, API keys, or other secrets.
MANUAL DEPTH · TOOL-ASSISTED COVERAGE
SecurityCipher offers freelance security work - manual and tool-assisted penetration testing for web applications, APIs, networks, mobile apps, cloud environments, and AI systems. Every engagement starts with written rules of engagement and ends with prioritized findings, proof, root-cause guidance, and a retest.
Manual web application penetration testing for authentication, authorization, business logic, injection, server-side, and browser security flaws.
Manual API penetration testing for authorization, authentication, business logic, and data exposure flaws that automated scanners routinely miss.
External and internal network penetration testing that validates exposed services, identity attack paths, segmentation, and the controls meant to stop lateral movement.
Cloud penetration testing for exploitable IAM paths, public exposure, workload identities, secrets, network boundaries, and control-plane weaknesses.
Android and iOS penetration testing across application packages, local data, runtime behavior, platform controls, deep links, and backend APIs.
Adversarial security testing for AI applications, chatbots, RAG systems, autonomous agents, tool use, and Model Context Protocol integrations.
Desktop and thick client penetration testing for binaries, local storage, update mechanisms, IPC, custom protocols, backend trust, and privilege boundaries.
Embedded product security engineering for teams that need AppSec strategy, threat modeling, secure design, DevSecOps, vulnerability management, and developer guidance.
External attack surface assessment that discovers internet-facing assets, ownership gaps, exposed services, leaked secrets, and high-value paths for manual validation.
Share your target, release date, and compliance objective to receive a tailored freelance scope.
WHY EXPERT-LED TESTING
The work is optimized for exploitability, engineering clarity, and verified remediation.
Automated coverage is followed by manual verification. Business logic, chained attacks, authorization boundaries, and product context receive dedicated testing.
Each finding explains affected assets, preconditions, reproduction steps, impact, severity rationale, root cause, and practical remediation.
Reports can map relevant findings to OWASP, NIST, PTES, SOC 2, ISO 27001, PCI DSS, or other agreed requirements without pretending a pentest is the audit itself.
One retest round is included. The updated report records closed, partially fixed, accepted, and still-open findings so residual risk is visible.
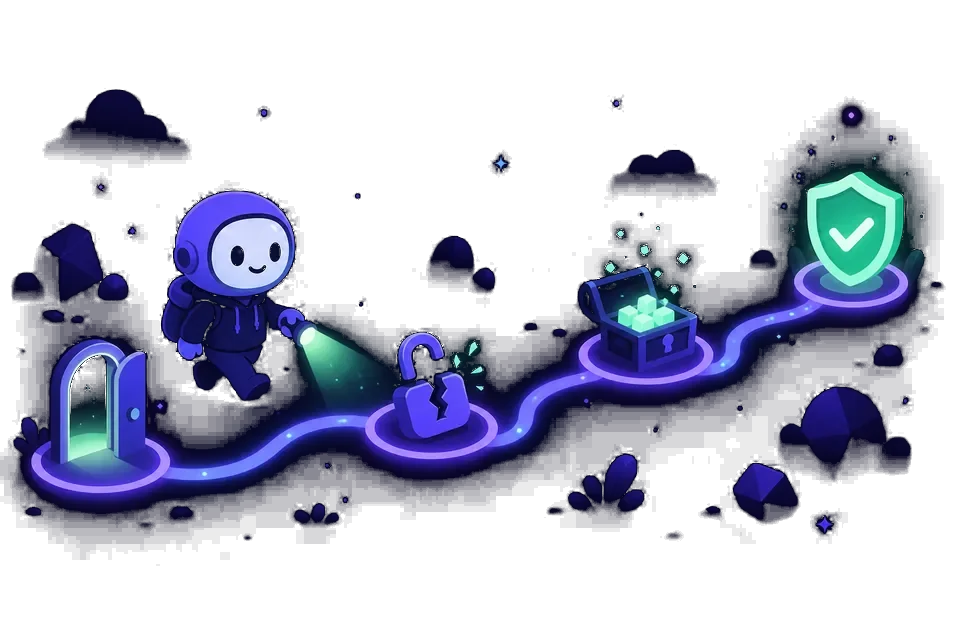
FROM EXPOSURE TO VERIFIED FIX
Testing connects the exposed entry point, the broken control, the reachable asset, and the remediation that breaks the path.
FROM SCOPE TO RETEST
A controlled engagement from scope to verified remediation
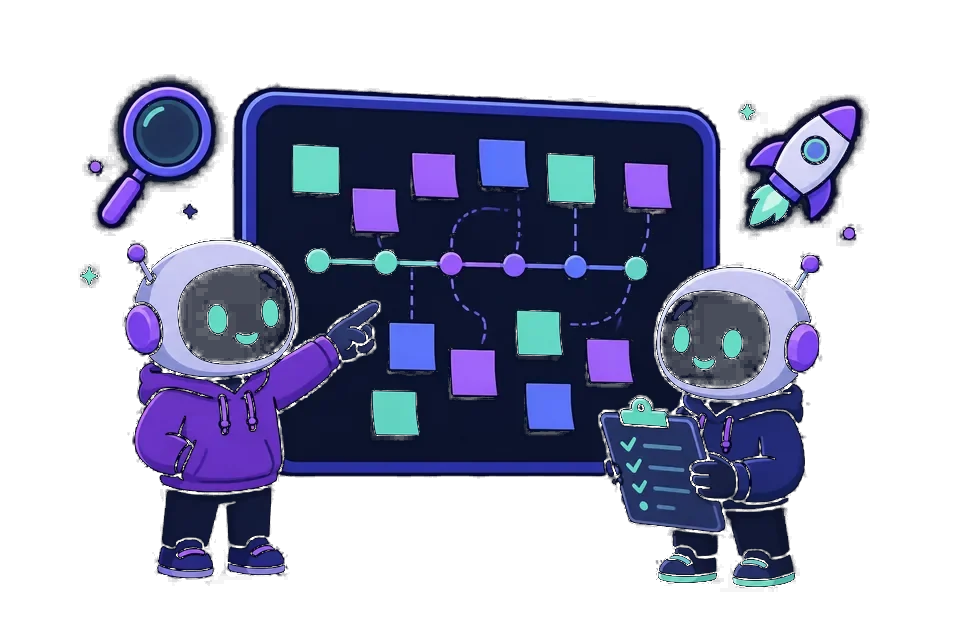
SCOPING IS PART OF THE TEST
Targets, roles, environments, test windows, and escalation contacts are agreed first, so testing stays predictable for your team and useful for your release plan.
Define objectives, targets, environments, credentials, excluded actions, test windows, data handling, escalation contacts, and explicit stop conditions.
Map identities, sensitive data, entry points, trust boundaries, dependencies, and likely abuse paths so testing reflects how the product actually works.
Use repeatable checks for breadth, then manually test authorization, business logic, state transitions, chained weaknesses, and controls that need human context.
Confirm exploitability with the minimum proof needed. Production stability and confidentiality take priority over collecting unnecessary data or pushing an exploit too far.
Deliver an executive summary, detailed findings, evidence, severity rationale, and root-cause fixes, followed by a walkthrough with security and engineering stakeholders.
Answer implementation questions and retest agreed fixes. The final status shows which attack paths are closed and where residual risk remains.
REPORTING THAT SURVIVES REVIEW
Useful to product leaders, security reviewers, developers, and auditors without turning the report into a scanner export.
Scope, overall risk, attack themes, business impact, and prioritized decisions without burying stakeholders in raw scanner output.
Severity, affected assets, preconditions, reproduction steps, evidence, impact, root cause, and implementation-focused remediation.
Tested roles, surfaces, standards, assumptions, exclusions, and constraints so readers understand what the assessment does and does not prove.
A revised status for remediated findings, including partial fixes and remaining attack paths rather than a blanket pass statement.
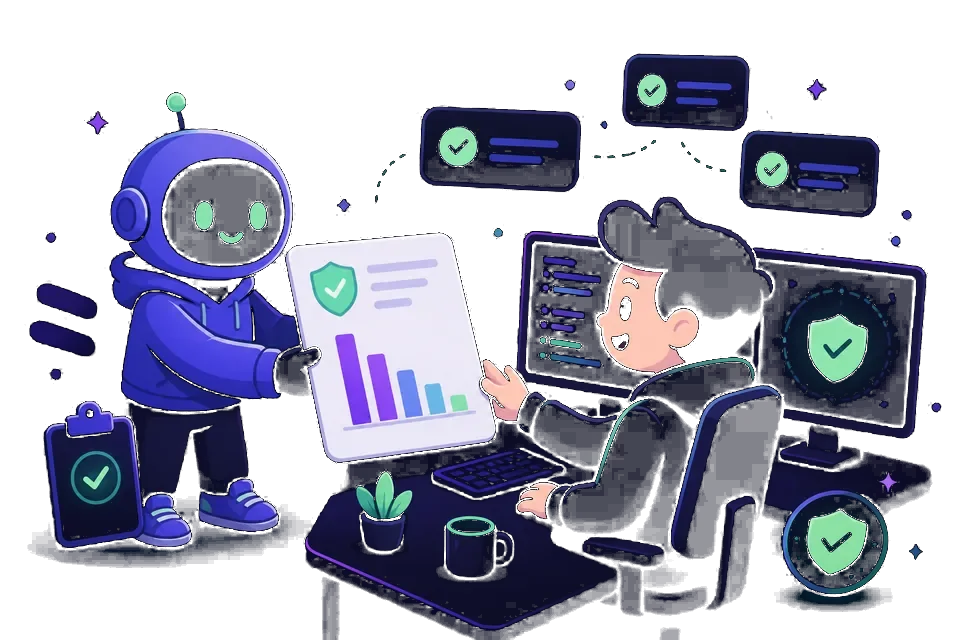
WRITTEN FOR THE PEOPLE WHO FIX IT
Each finding carries reproduction steps, evidence, root cause, and a fix that matches your stack - plus a summary a non-technical stakeholder can read in one sitting.
Standards shape coverage and reporting. The actual test is adapted to your architecture, roles, data flows, and business logic.
TRANSPARENT STARTING POINTS
IDENTITY, EXPERIENCE, ACCOUNTABILITY
Your freelance assessment is led by Piyush Kumawat, Staff Product Security Engineer and penetration tester
Piyush has assessed 300+ web, mobile, and API applications across startup, SaaS, fintech, and enterprise environments. His freelance security work spans hands-on offensive testing, product security, threat modeling, DevSecOps, and cloud security.
SecurityCipher combines hands-on freelance testing with product security, threat modeling, DevSecOps, cloud, and AI security experience. The engagement is not handed to an anonymous testing pool.
PUBLIC METHODOLOGY · NO BLACK BOX
SecurityCipher publishes practical methodology and checklists so you can evaluate the depth behind the service.
COMMON BUYER QUESTIONS
Scope, timing, reports, compliance, and retesting
Yes. SecurityCipher provides freelance security and penetration testing for startups, SaaS teams, and product companies that need focused, expert-led testing without a large consulting firm. Scopes cover web, API, mobile, cloud, network, AI, and product security work.
Most focused web and API assessments take 5-10 business days after scope and access are ready. Mobile, cloud, network, and multi-application reviews vary with assets, roles, environments, and depth. The proposal includes a testing and reporting timeline.
Every engagement includes an executive summary, scope and coverage record, detailed findings with evidence and severity rationale, reproduction steps, root-cause remediation guidance, and one retest update for agreed fixes.
Yes. Client credentials, target details, evidence, and reports are handled as confidential engagement data. Your standard NDA and security requirements can be reviewed during scoping.
Yes. One retest round is included for validated findings fixed within the agreed window. The updated report records closed, partially fixed, accepted, and still-reproducible issues.
A vulnerability scan uses signatures and automated checks to identify probable weaknesses. Penetration testing manually verifies exploitability, tests business and authorization logic, and can chain weaknesses to demonstrate impact within agreed safety limits.
Yes, when the scope and report format are agreed in advance. A pentest can provide technical assurance evidence and map findings to relevant controls, but it does not replace the broader audit, governance program, or Qualified Security Assessor where one is required.
Yes. Scopes range from a focused pre-launch application review to multi-surface product and infrastructure testing. The same reporting standard applies, while access, coordination, and testing depth are adjusted to the engagement.
Yes, when production testing is appropriate and explicitly authorized. Rules of engagement define rate limits, test accounts, prohibited actions, monitoring contacts, and stop conditions. Disruptive techniques are excluded or moved to staging.
CLEAR SCOPE · CONTROLLED TESTING · VERIFIED FIXES
Share the target type, environment, roles, and objective. You will receive a recommended scope and written assumptions before testing begins.