
SecurityCipher
Home Blog About Us

Learn Paths, courses, and reference docs

  • 🚀 Start Here Beginner path through the site
  • 🗺️ Penetration Testing Roadmap Structured path to become a pentester
  • 🎓 Free Security Courses Current free Udemy coupon listings
  • 📄 Secure Code Explain Vulnerable vs secure code side by side
  • 🎯 Penetration Testing Tricks Field notes for real engagements
  • 📖 Vulnerability Explain How common vulns actually work

Checklists Interactive reviews and LLM risks

  • ✅ Security Checklists Hub All interactive security checklists
  • 📋 Writeup Checklists Steps derived from real writeups
  • 🧠 LLM AI Security Checklist Controls for LLM apps
  • 🤖 OWASP LLM Top 10 LLM Top 10 risks mapped out
  • 🧰 Burp Suite Guide Step-by-step Burp tutorials
  • 📘 Payload Field Manual Safe-first probes and signals

Practice Browser labs, games, and explorers

  • 🔬 Interactive Labs SQL injection, AI, architecture review
  • 🎮 Security Games Phishing, JWT, WAF, and more
  • 🚗 On-Call Drive Neon-city arcade security missions
  • • Shift Zero SOC desk: phish, OTP, malware, tickets
  • ❓ Application Security Quiz Web, secure coding, and cloud quizzes
  • 🗺️ OWASP Top 10 Explorer Clickable risk map with signals
  • 🔀 Interactive Attack Paths Recon-to-impact chains

Tools & Career Databases, jobs, and community

  • 🛠️ Security Tools Curated recon, SAST, and bounty tools
  • 🔎 CVE Lookup Multi-source CVE intelligence
  • 💰 Bug Bounty Programs Live public scopes to search
  • 💼 Cybersecurity Jobs Roles from company career pages
  • 🧑‍💻 Security Researchers Community profiles and submissions
  • 🎤 Security Conferences Upcoming and past events
Browse all Security resources hub Freelance Security →
My Resume
Freelance SecurityFreelance
New Security Researchers Join the directory - submit your profile for review Submit profile →
← Security Tools View on GitHub

bettercap

Swiss-army knife for network attacks and monitoring, including MITM, Wi-Fi, BLE and Ethernet.

Join the project community on our server!

BetterCap

Release Software License Tests on Linux Tests on macOS Tests on Windows Docker Hub This project is 100% made by humans.

bettercap is a powerful, easily extensible and portable framework written in Go which aims to offer to security researchers, red teamers and reverse engineers an easy to use, all-in-one solution with all the features they might possibly need for performing reconnaissance and attacking WiFi networks, Bluetooth Low Energy devices, CAN-bus, wireless HID devices and Ethernet networks.
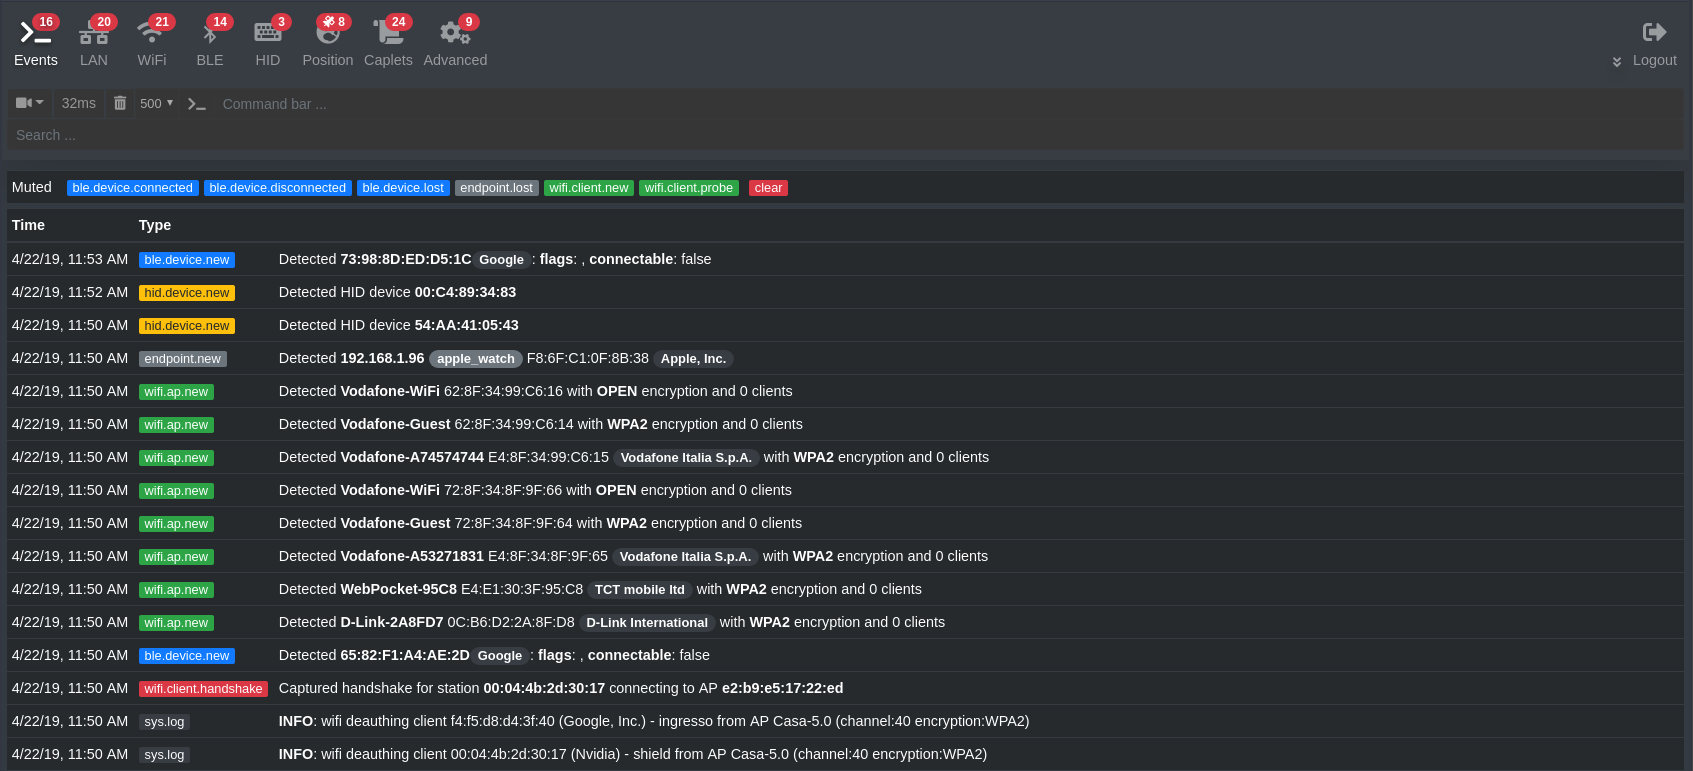
UI

Main Features

  • WiFi networks scanning, deauthentication attack, clientless PMKID association attack and automatic WPA/WPA2/WPA3 client handshakes capture.
  • Bluetooth Low Energy devices scanning, characteristics enumeration, reading and writing.
  • 2.4Ghz wireless devices scanning and MouseJacking attacks with over-the-air HID frames injection (with DuckyScript support).
  • CAN-bus and DBC support for decoding, injecting and fuzzing frames.
  • Passive and active IP network hosts probing and recon.
  • ARP, DNS, NDP and DHCPv6 spoofers for MITM attacks on IPv4 and IPv6 based networks.
  • Proxies at packet level, TCP level and HTTP/HTTPS application level fully scriptable with easy to implement javascript plugins.
  • A powerful network sniffer for credentials harvesting which can also be used as a network protocol fuzzer.
  • A very fast port scanner.
  • A powerful REST API with support for asynchronous events notification on websocket to orchestrate your attacks easily.
  • A very convenient web UI.
  • More!

Contributors

bettercap project contributors

License

bettercap is made with ♥ and released under the GPL 3 license.

Stargazers over time

Stargazers over time

Press Escape to close the search panel.

Donate

Buy me a Coffee

Penetration Testing Services

penetration Testing Services

Web Application Security Quiz

Web Application Security Quiz

Daily Bug Bounty Writeups - Twitter

Daily Bug Bounty Writeups

Download our Latest Android Application

Guide for Penetration Testing

Daily Bug Bounty Writeups - Telegram

Daily Bug Bounty Writeups

Author

Piyush
Senior Product Security Engineer

Ethical Hacker || Penetration Tester || Gamer || Blogger || Product Security Engineer || AI Security

READ ARTICLE

Donate

Buy me a Coffee

Recent Posts

  • AI-Generated Code Security Bugs: A Vibe Coding Case Study
    AI-Generated Code Security Bugs: A Vibe Coding Case Study
    October 7, 2026/
    0 Comments
  • Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    September 8, 2026/
    0 Comments
  • DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    August 27, 2026/
    0 Comments

Follow Us

SecurityCipher

Practical security guides, vulnerability deep-dives, and hands-on resources for bug bounty hunters and penetration testers.

Useful Links

  • Security Checklists
  • Cybersecurity Jobs
  • Blogs
  • About
  • Contact
© 2026 Security Cipher. All rights reserved. Privacy Policy · Terms & Conditions