SecurityCipher
Home Blog About Us

Learn Paths, courses, and reference docs

  • 🚀 Start Here Beginner path through the site
  • 🗺️ Penetration Testing Roadmap Structured path to become a pentester
  • 🎓 Free Security Courses Current free Udemy coupon listings
  • 📄 Secure Code Explain Vulnerable vs secure code side by side
  • 🎯 Penetration Testing Tricks Field notes for real engagements
  • 📖 Vulnerability Explain How common vulns actually work

Checklists Interactive reviews and LLM risks

  • ✅ Security Checklists Hub All interactive security checklists
  • 📋 Writeup Checklists Steps derived from real writeups
  • 🧠 LLM AI Security Checklist Controls for LLM apps
  • 🤖 OWASP LLM Top 10 LLM Top 10 risks mapped out
  • 🧰 Burp Suite Guide Step-by-step Burp tutorials
  • 📘 Payload Field Manual Safe-first probes and signals

Practice Browser labs, games, and explorers

  • 🔬 Interactive Labs SQL injection, AI, architecture review
  • 🎮 Security Games Phishing, JWT, WAF, and more
  • 🚗 On-Call Drive Neon-city arcade security missions
  • • Shift Zero SOC desk: phish, OTP, malware, tickets
  • ❓ Application Security Quiz Web, secure coding, and cloud quizzes
  • 🗺️ OWASP Top 10 Explorer Clickable risk map with signals
  • 🔀 Interactive Attack Paths Recon-to-impact chains

Tools & Career Databases, jobs, and community

  • 🛠️ Security Tools Curated recon, SAST, and bounty tools
  • 🔎 CVE Lookup Multi-source CVE intelligence
  • 💰 Bug Bounty Programs Live public scopes to search
  • 💼 Cybersecurity Jobs Roles from company career pages
  • 🧑‍💻 Security Researchers Community profiles and submissions
  • 🎤 Security Conferences Upcoming and past events
Browse all Security resources hub Freelance Security →
My Resume
Freelance SecurityFreelance
New Security Researchers Join the directory - submit your profile for review Submit profile →
← Security Tools View on GitHub

CrowdSec

Collaborative IPS that analyzes behavior and shares signals to block attacks.

CrowdSec

CrowdSec: open-source IDS/IPS, WAF and bot detection

CrowdSec is an open-source and participative security solution offering crowdsourced server detection and protection against malicious IPs. Detect and block with our Security Engine, contribute to the network, and enjoy our real-time community blocklist.

CrowdSec schema

Features & Advantages

Versatile Security Engine

CrowdSec Security Engine is an all-in-one IDS/IPS and WAF.

It detects bad behaviors by analyzing log sources and HTTP requests, and allows active remediation thanks to the Remediation Components.

Detection rules are available on our hub under MIT license.

CrowdSec Community Blocklist

The "Community Blocklist" is a curated list of IP addresses identified as malicious by CrowdSec. The Security Engine proactively blocks the IP addresses of this blocklist, preventing malevolent IPs from reaching your systems.
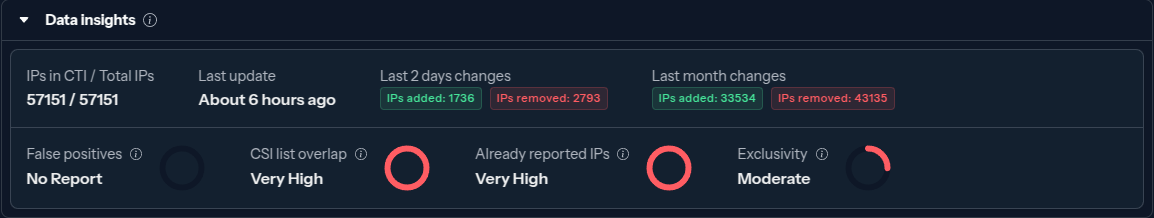
CrowdSec Community Blocklist

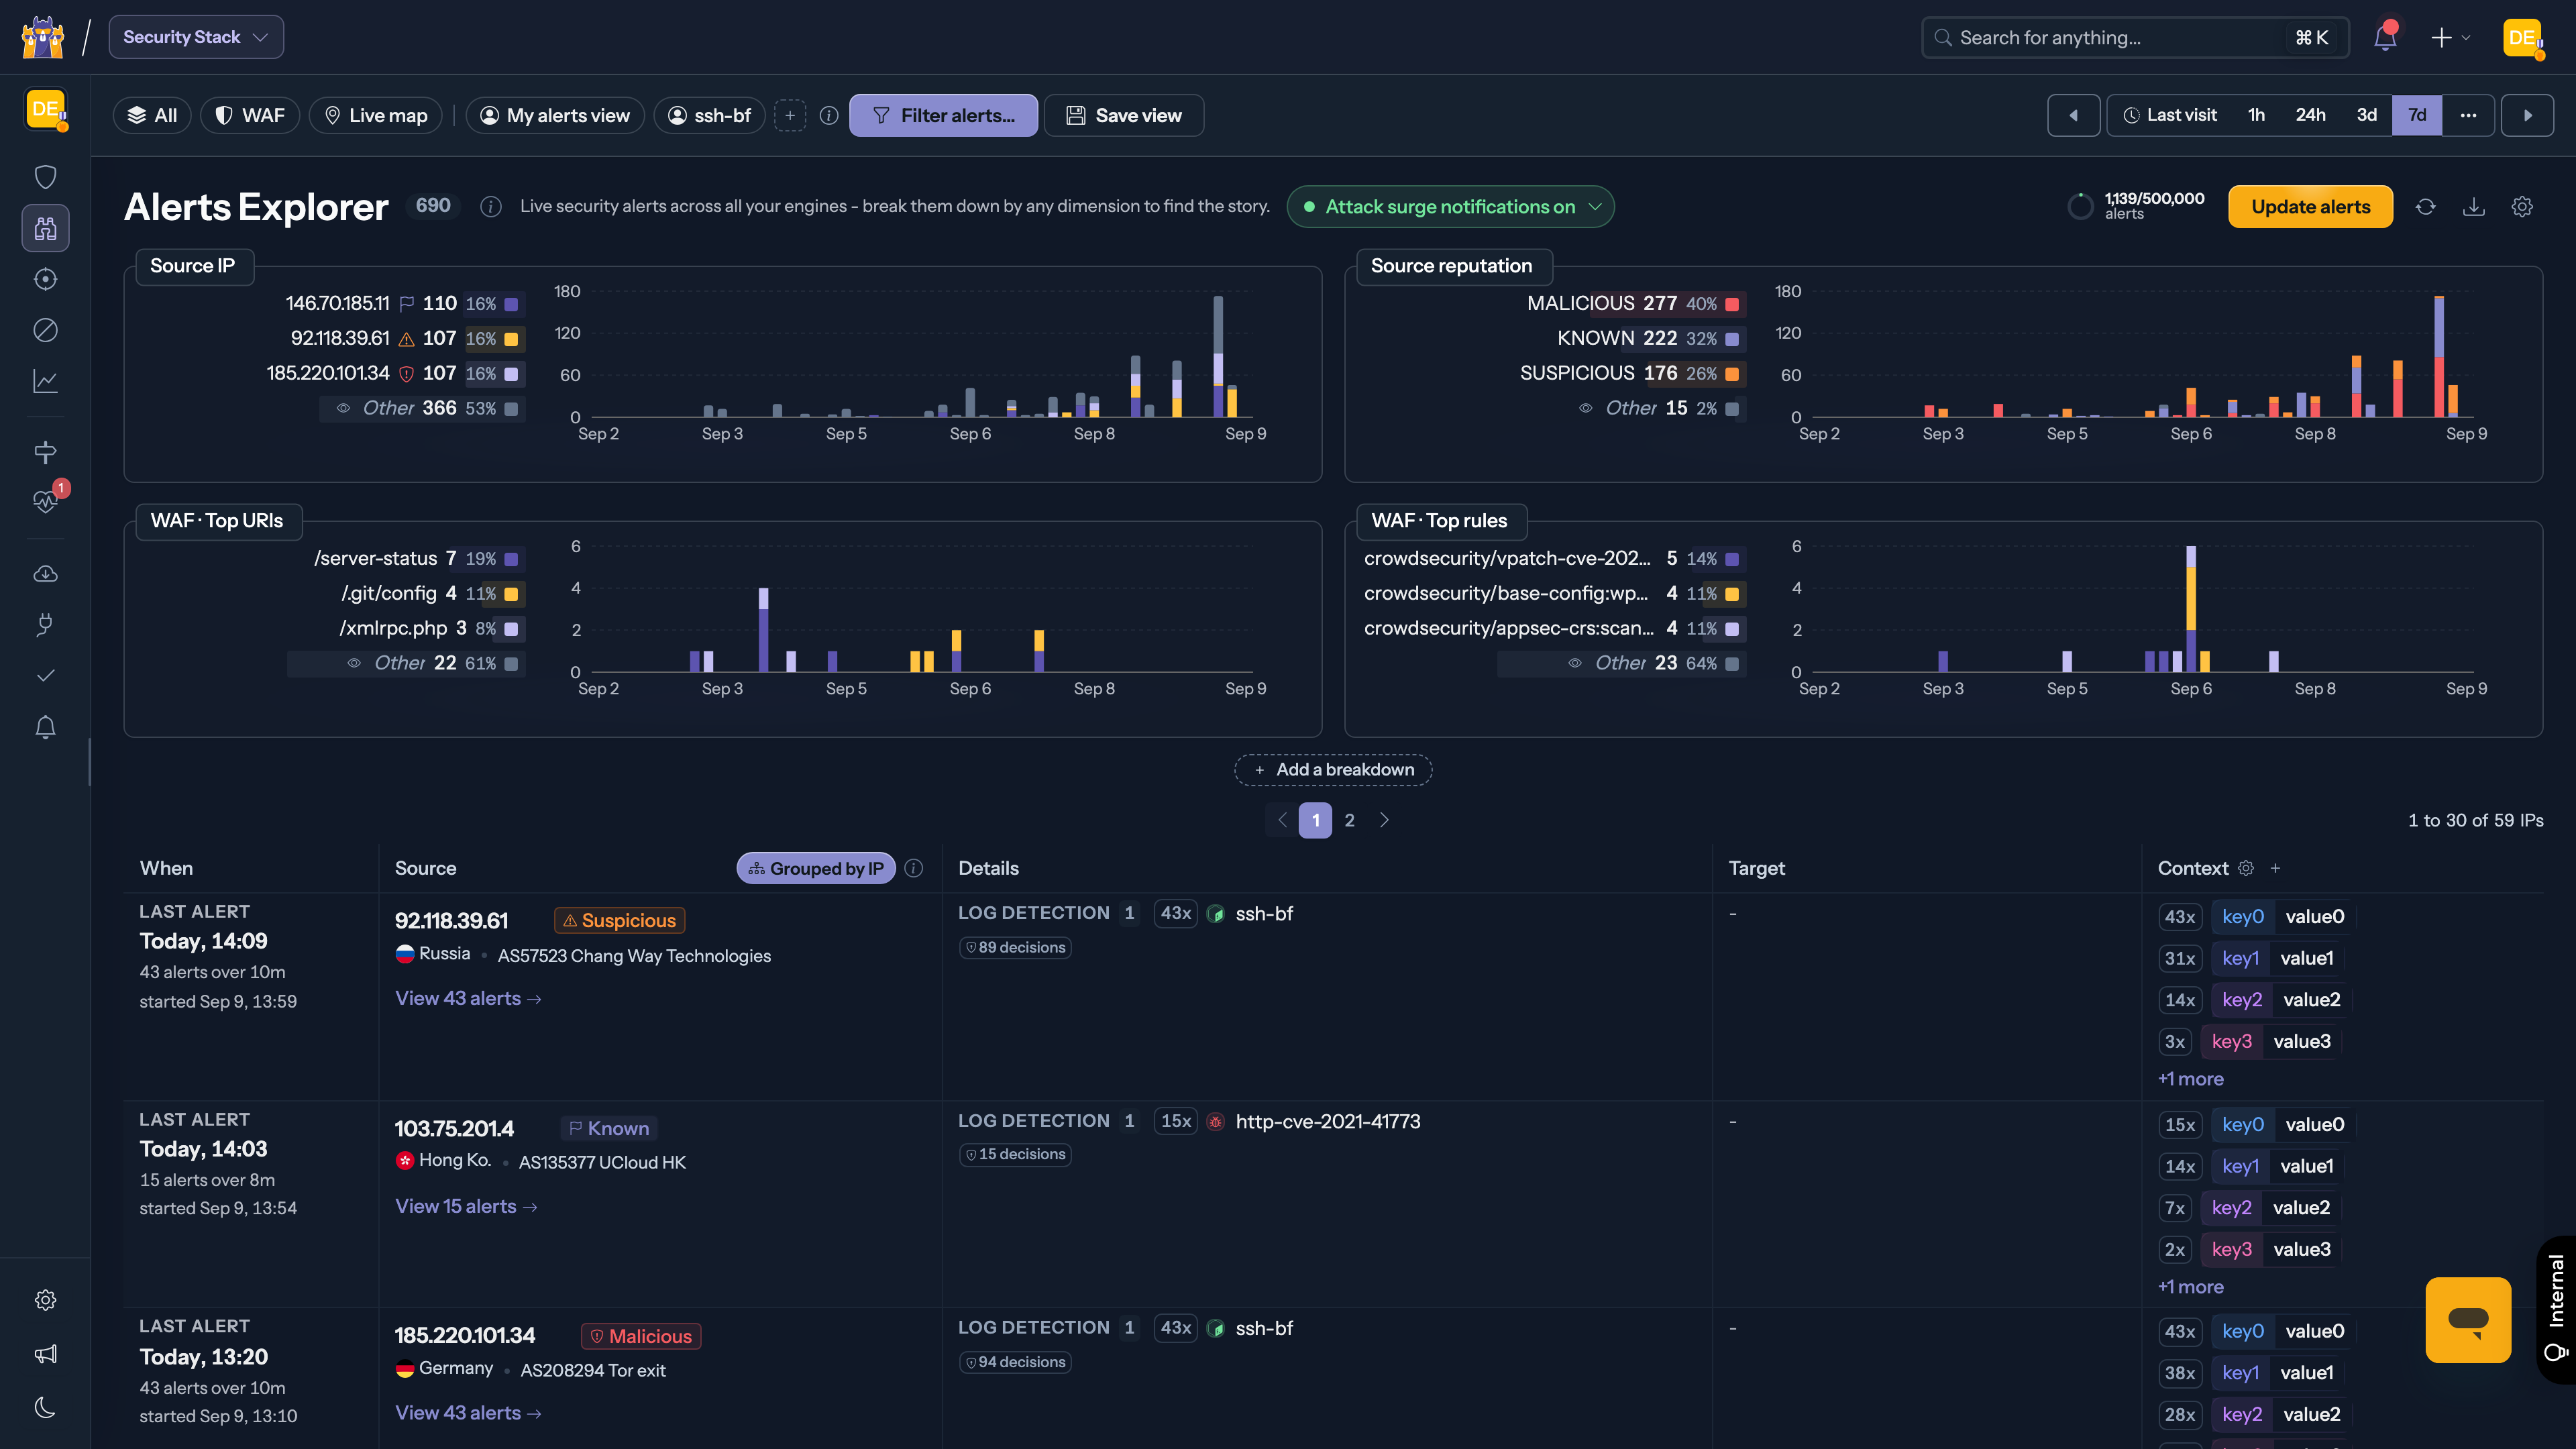
Console - Monitoring & Automation of your security stack

CrowdSec Console

Multiple Platforms support

Multiple Platforms support

How CrowdSec compares

To fail2ban — CrowdSec reads the same log files and bans the same IPs, but detection and remediation are decoupled: parse logs on one machine, block at the firewall, reverse proxy or CDN on another. Attacks you report feed a community blocklist, so an IP that hits one user gets blocked for everyone else before it reaches them.

To ModSecurity, Coraza and naxsi — the AppSec component is a WAF built on Coraza, so SecLang rules and the OWASP Core Rule Set load as-is. On top of that it adds a YAML rule format, and shares the IP reputation and remediation layer with the log-based engine.

Bot and scraper detection — AppSec can answer a suspicious request with a JavaScript proof-of-work challenge at a tunable difficulty, which stops headless browsers and scrapers while letting verified crawlers such as Googlebot through.

Outnumbering hackers all together

By sharing the threat they faced, all users are protecting each other (hence the name Crowd-Security). Crowdsec is designed for modern infrastructures, with its "Detect Here, Remedy There" approach, letting you analyze logs coming from several sources in one place and block threats at various levels (applicative, system, infrastructural) of your stack.

CrowdSec ships by default with scenarios (brute force, port scan, web scan, etc.) adapted for most contexts, but you can easily extend it by picking more of them from the HUB. It is also easy to adapt an existing one or create one yourself.

Installation

Follow our documentation to install CrowdSec in a few minutes on Linux, Windows, Docker, OpnSense, Kubernetes, and more.

Resources

  • Console: Supercharge your CrowdSec setup with visualization, management capabilities, extra blocklists and premium features.
  • Documentation: Learn how to exploit your CrowdSec setup to deter more attacks.
  • Discord: A question or a suggestion? This is the place.
  • Hub: Improve your stack protection, find the relevant remediation components for your infrastructure.
  • Public Roadmap: Vote for your favorite features and submit ideas to influence what we build next.
  • CrowdSec Academy: Learn and grow with our courses.
  • Corporate Website: For everything else.
Press Escape to close the search panel.

Donate

Buy me a Coffee

Penetration Testing Services

penetration Testing Services

Web Application Security Quiz

Web Application Security Quiz

Daily Bug Bounty Writeups - Twitter

Daily Bug Bounty Writeups

Download our Latest Android Application

Guide for Penetration Testing

Daily Bug Bounty Writeups - Telegram

Daily Bug Bounty Writeups

Author

Piyush
Senior Product Security Engineer

Ethical Hacker || Penetration Tester || Gamer || Blogger || Product Security Engineer || AI Security

READ ARTICLE

Donate

Buy me a Coffee

Recent Posts

  • AI-Generated Code Security Bugs: A Vibe Coding Case Study
    AI-Generated Code Security Bugs: A Vibe Coding Case Study
    October 7, 2026/
    0 Comments
  • Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    September 8, 2026/
    0 Comments
  • DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    August 27, 2026/
    0 Comments

Follow Us

SecurityCipher

Practical security guides, vulnerability deep-dives, and hands-on resources for bug bounty hunters and penetration testers.

Useful Links

  • Security Checklists
  • Cybersecurity Jobs
  • Blogs
  • About
  • Contact
© 2026 Security Cipher. All rights reserved. Privacy Policy · Terms & Conditions