SecurityCipher
Home Blog About Us

Learn Paths, courses, and reference docs

  • 🚀 Start Here Beginner path through the site
  • 🗺️ Penetration Testing Roadmap Structured path to become a pentester
  • 🎓 Free Security Courses Current free Udemy coupon listings
  • 📄 Secure Code Explain Vulnerable vs secure code side by side
  • 🎯 Penetration Testing Tricks Field notes for real engagements
  • 📖 Vulnerability Explain How common vulns actually work

Checklists Interactive reviews and LLM risks

  • ✅ Security Checklists Hub All interactive security checklists
  • 📋 Writeup Checklists Steps derived from real writeups
  • 🧠 LLM AI Security Checklist Controls for LLM apps
  • 🤖 OWASP LLM Top 10 LLM Top 10 risks mapped out
  • 🧰 Burp Suite Guide Step-by-step Burp tutorials
  • 📘 Payload Field Manual Safe-first probes and signals

Practice Browser labs, games, and explorers

  • 🔬 Interactive Labs SQL injection, AI, architecture review
  • 🎮 Security Games Phishing, JWT, WAF, and more
  • 🚗 On-Call Drive Neon-city arcade security missions
  • • Shift Zero SOC desk: phish, OTP, malware, tickets
  • ❓ Application Security Quiz Web, secure coding, and cloud quizzes
  • 🗺️ OWASP Top 10 Explorer Clickable risk map with signals
  • 🔀 Interactive Attack Paths Recon-to-impact chains

Tools & Career Databases, jobs, and community

  • 🛠️ Security Tools Curated recon, SAST, and bounty tools
  • 🔎 CVE Lookup Multi-source CVE intelligence
  • 💰 Bug Bounty Programs Live public scopes to search
  • 💼 Cybersecurity Jobs Roles from company career pages
  • 🧑‍💻 Security Researchers Community profiles and submissions
  • 🎤 Security Conferences Upcoming and past events
Browse all Security resources hub Freelance Security →
My Resume
Freelance SecurityFreelance
New Security Researchers Join the directory - submit your profile for review Submit profile →
← Security Tools View on GitHub

MobSF

Automated mobile app (Android/iOS/Windows) security assessment framework for static and dynamic analysis.

Mobile Security Framework (MobSF)

Mobile Security Framework (MobSF) is a security research platform for mobile applications in Android, iOS and Windows Mobile. MobSF can be used for a variety of use cases such as mobile application security, penetration testing, malware analysis, and privacy analysis. The Static Analyzer supports popular mobile app binaries like APK, IPA, APPX and source code. Meanwhile, the Dynamic Analyzer supports both Android and iOS applications and offers a platform for interactive instrumented testing, runtime data and network traffic analysis. MobSF seamlessly integrates with your DevSecOps or CI/CD pipeline, facilitated by REST APIs and CLI tools, enhancing your security workflow with ease.

Made with Love in India

Docker Pulls python PyPI version platform License MobSF tests Quality Gate Status GitHub closed issues CII Best Practices

ToolsWatch Best Security Tools 2016 ToolsWatch Best Security Tools 2017 Blackhat Arsenal Asia 2015 Blackhat Arsenal Asia 2018 Blackhat Arsenal Europe 2023

MobSF is also bundled with Android Tamer, BlackArch and Pentoo.

Support MobSF

Donate to MobSF

Has MobSF made a difference for you? Show your support and help us innovate with a donation. It's easy to build open source, maintaining one is a different story.

Long live open source!

Documentation

Quick setup with docker

docker pull opensecurity/mobile-security-framework-mobsf:latest
docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest

# Default username and password: mobsf/mobsf

See MobSF Documentation

  • Try MobSF Static Analyzer Online: mobsf.live
  • MobSF in CI/CD: mobsfscan
  • Conference Presentations: Slides & Videos
  • MobSF Online Course: OpSecX MAS
  • What's New: See Changelog

Collaborators

Ajin Abraham india | Magaofei china | Matan Dobrushin israel | Vincent Nadal france

e-Learning Courses & Certifications

MobSF Course Automated Mobile Application Security Assessment with MobSF -MAS

Android Security Tools Course Android Security Tools Expert -ATX

MobSF Support

  • Free Support: Free limited support, questions, help and discussions, join our Slack channel Join_MobSF_Slack
  • Enterprise Support: Priority feature requests, live support & onsite training, see MobSF Support Packages
Contribution, Feature Requests & Bugs

  • Read CONTRIBUTING.md before opening bugs, feature requests and pull request.
  • For Project updates and announcements, follow @ajinabraham or @OpenSecurity_IN.
  • Github Issues are only for tracking bugs and feature requests. Do not post support or help queries there. We have a slack channel for that.
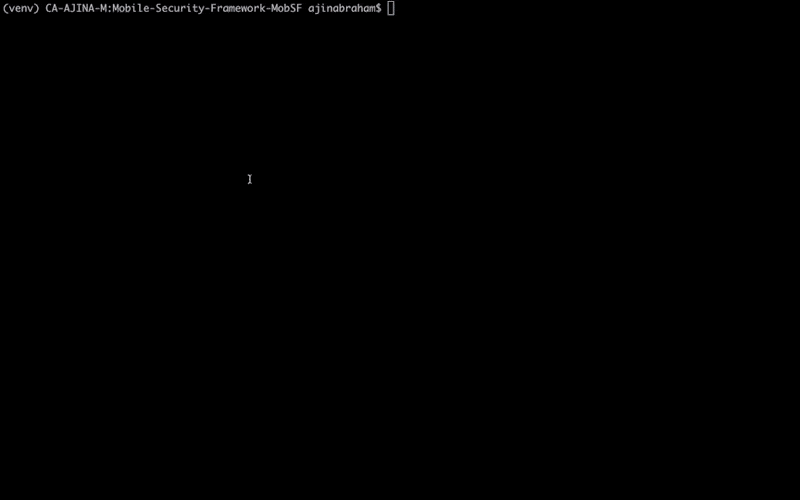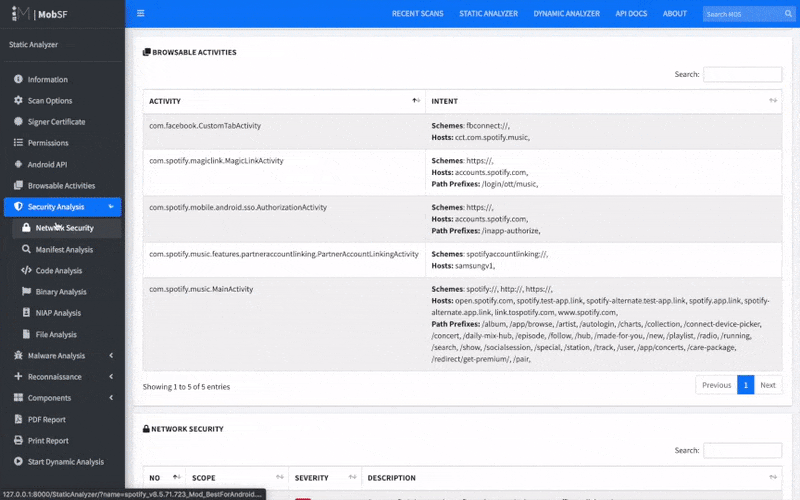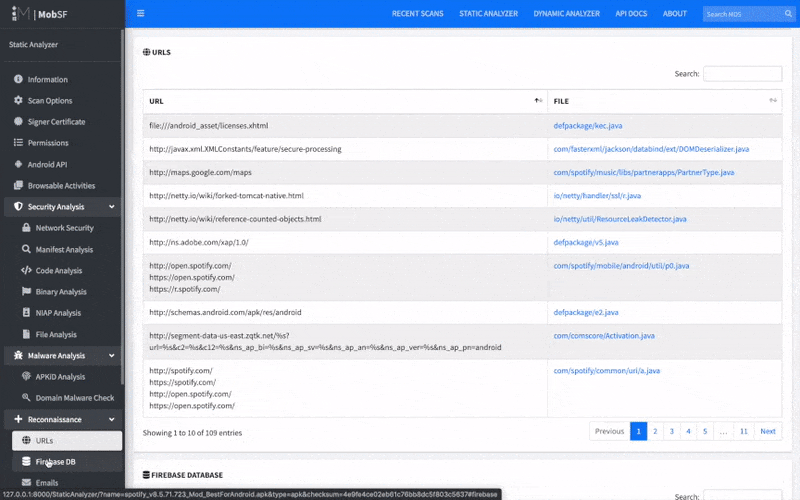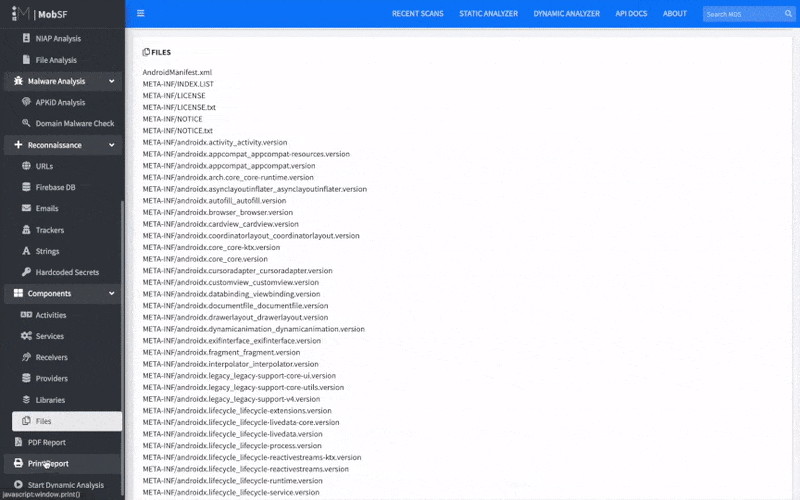
Static Analysis - Android

mobsf_android_static_analysis

Static Analysis - iOS

mobsf_ios_ipa_static_analysis

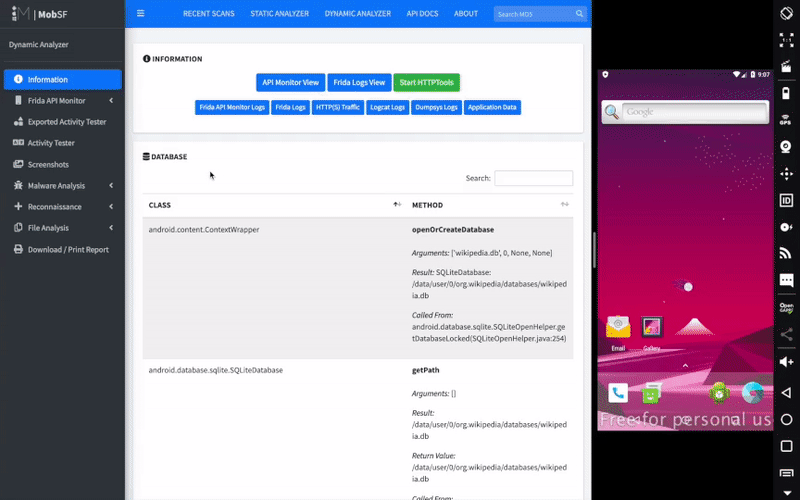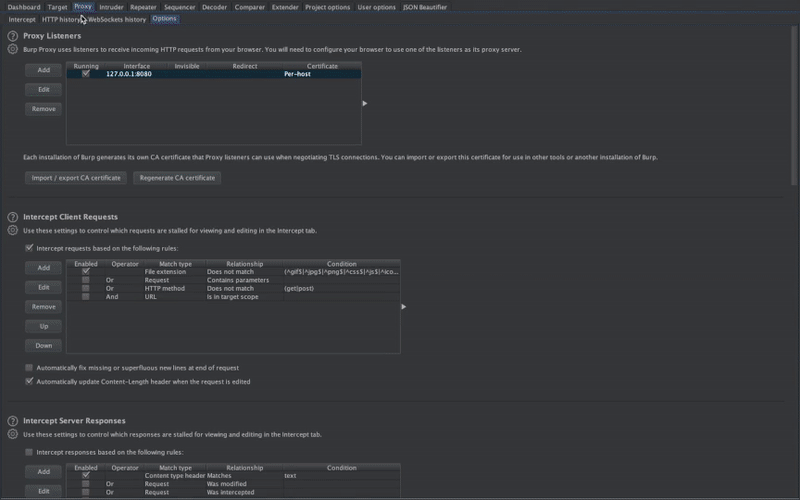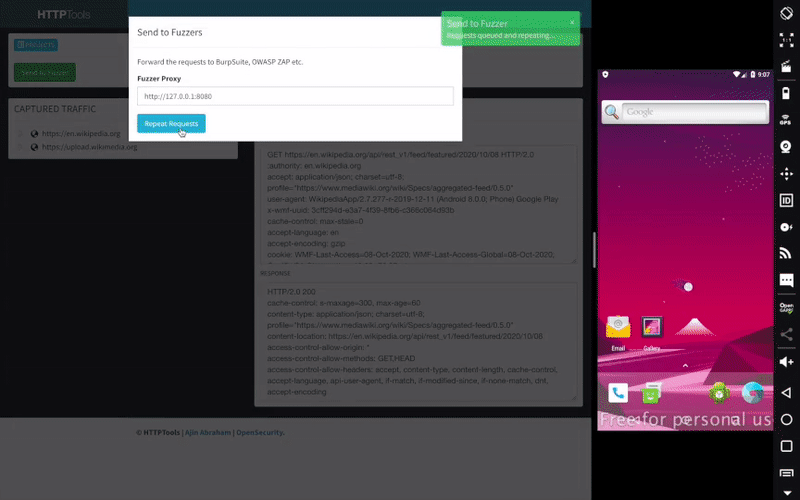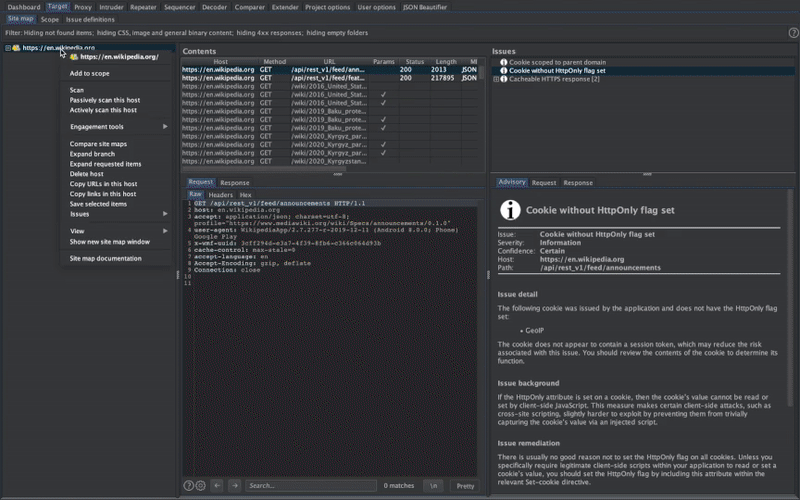
Dynamic Analysis - Android APK

mobsf_android_dynamic_analysis

Web API Viewer

mobsf_web_api_fuzzing_with_burp

Dynamic Analysis - iOS IPA

mobsf_ios_dynamic_analysis

Past Collaborators

  • Dominik Schlecht germany

Honorable Contributors & Shoutouts

  • Amrutha VC - For the new MobSF logo
  • Dominik Schlecht - For the awesome work on adding Windows Phone App Static Analysis to MobSF
  • Esteban - Better Android Manifest Analysis and Static Analysis Improvement.
  • Matan Dobrushin - For adding Android ARM Emulator support to MobSF - Special thanks goes for cuckoo-droid
  • Shuxin - Android Binary Analysis
  • Abhinav Saxena - (@xandfury) - For Travis CI and Logging integration
  • netguru Netguru (@karolpiateknet, @mtbrzeski) - For iOS Swift support, Rule contributions and SAST refactoring.
  • Maxime Fawe - (@Arenash13) - For Matching Strategy implementation of SAST pattern matching algorithms.
  • Abhinav Sejpal (@Abhinav_Sejpal) - For poking me with bugs, feature requests, and UI & UX suggestions
  • Anant Srivastava (@anantshri) - For Activity Tester Idea
  • Anto Joseph (@antojoseph) - For the help with SuperSU
  • Bharadwaj Machiraju (@tunnelshade) - For writing pyWebProxy from scratch
  • Rahul (@c0dist) - Kali Support
  • MindMac - For writing Android Blue Pill
  • Oscar Alfonso Diaz - (@OscarAkaElvis) - For Dockerfile contributions
  • Thomas Abraham - For JS Hacks on UI
  • Tim Brown (@timb_machine) - For the iOS Binary Analysis Ruleset
  • Shanil Prasad (@Rajuraju14) - For improving iOS ATS Analysis
  • Jovan Petrovic (@JovanPetrovic) - For sponsoring a server to host mobsf.live
Press Escape to close the search panel.

Donate

Buy me a Coffee

Penetration Testing Services

penetration Testing Services

Web Application Security Quiz

Web Application Security Quiz

Daily Bug Bounty Writeups - Twitter

Daily Bug Bounty Writeups

Download our Latest Android Application

Guide for Penetration Testing

Daily Bug Bounty Writeups - Telegram

Daily Bug Bounty Writeups

Author

Piyush
Senior Product Security Engineer

Ethical Hacker || Penetration Tester || Gamer || Blogger || Product Security Engineer || AI Security

READ ARTICLE

Donate

Buy me a Coffee

Recent Posts

  • AI-Generated Code Security Bugs: A Vibe Coding Case Study
    AI-Generated Code Security Bugs: A Vibe Coding Case Study
    October 7, 2026/
    0 Comments
  • Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    September 8, 2026/
    0 Comments
  • DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    August 27, 2026/
    0 Comments

Follow Us

SecurityCipher

Practical security guides, vulnerability deep-dives, and hands-on resources for bug bounty hunters and penetration testers.

Useful Links

  • Security Checklists
  • Cybersecurity Jobs
  • Blogs
  • About
  • Contact
© 2026 Security Cipher. All rights reserved. Privacy Policy · Terms & Conditions