
SecurityCipher
Home Blog About Us

Learn Paths, courses, and reference docs

  • ๐Ÿš€ Start Here Beginner path through the site
  • ๐Ÿ—บ๏ธ Penetration Testing Roadmap Structured path to become a pentester
  • ๐ŸŽ“ Free Security Courses Current free Udemy coupon listings
  • ๐Ÿ“„ Secure Code Explain Vulnerable vs secure code side by side
  • ๐ŸŽฏ Penetration Testing Tricks Field notes for real engagements
  • ๐Ÿ“– Vulnerability Explain How common vulns actually work

Checklists Interactive reviews and LLM risks

  • โœ… Security Checklists Hub All interactive security checklists
  • ๐Ÿ“‹ Writeup Checklists Steps derived from real writeups
  • ๐Ÿง  LLM AI Security Checklist Controls for LLM apps
  • ๐Ÿค– OWASP LLM Top 10 LLM Top 10 risks mapped out
  • ๐Ÿงฐ Burp Suite Guide Step-by-step Burp tutorials
  • ๐Ÿ“˜ Payload Field Manual Safe-first probes and signals

Practice Browser labs, games, and explorers

  • ๐Ÿ”ฌ Interactive Labs SQL injection, AI, architecture review
  • ๐ŸŽฎ Security Games Phishing, JWT, WAF, and more
  • ๐Ÿš— On-Call Drive Neon-city arcade security missions
  • โ€ข Shift Zero SOC desk: phish, OTP, malware, tickets
  • โ“ Application Security Quiz Web, secure coding, and cloud quizzes
  • ๐Ÿ—บ๏ธ OWASP Top 10 Explorer Clickable risk map with signals
  • ๐Ÿ”€ Interactive Attack Paths Recon-to-impact chains

Tools & Career Databases, jobs, and community

  • ๐Ÿ› ๏ธ Security Tools Curated recon, SAST, and bounty tools
  • ๐Ÿ”Ž CVE Lookup Multi-source CVE intelligence
  • ๐Ÿ’ฐ Bug Bounty Programs Live public scopes to search
  • ๐Ÿ’ผ Cybersecurity Jobs Roles from company career pages
  • ๐Ÿง‘โ€๐Ÿ’ป Security Researchers Community profiles and submissions
  • ๐ŸŽค Security Conferences Upcoming and past events
Browse all Security resources hub Freelance Security โ†’
My Resume
Freelance SecurityFreelance
New Security Researchers Join the directory - submit your profile for review Submit profile โ†’
← Security Tools View on GitHub

schemathesis

Property-based testing for APIs from OpenAPI and GraphQL schemas.

Build Coverage Version Python versions Discord License

Schemathesis

Catch API bugs before your users do.

Schemathesis tests OpenAPI and GraphQL APIs by generating inputs from your schema, adapting to server responses, and chaining operations into realistic workflows.
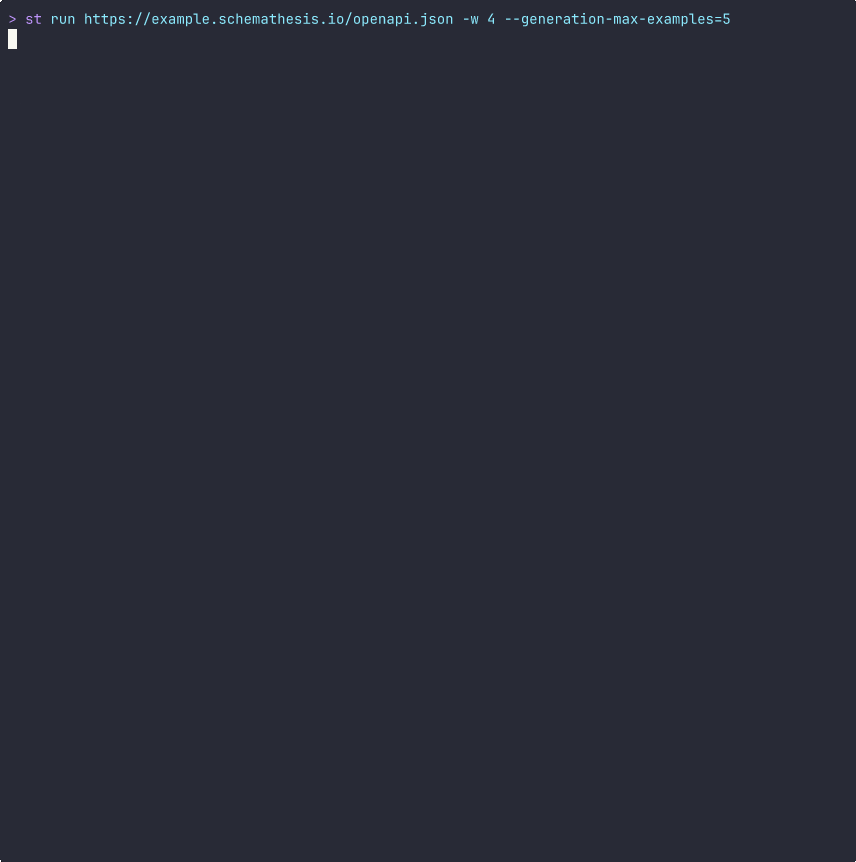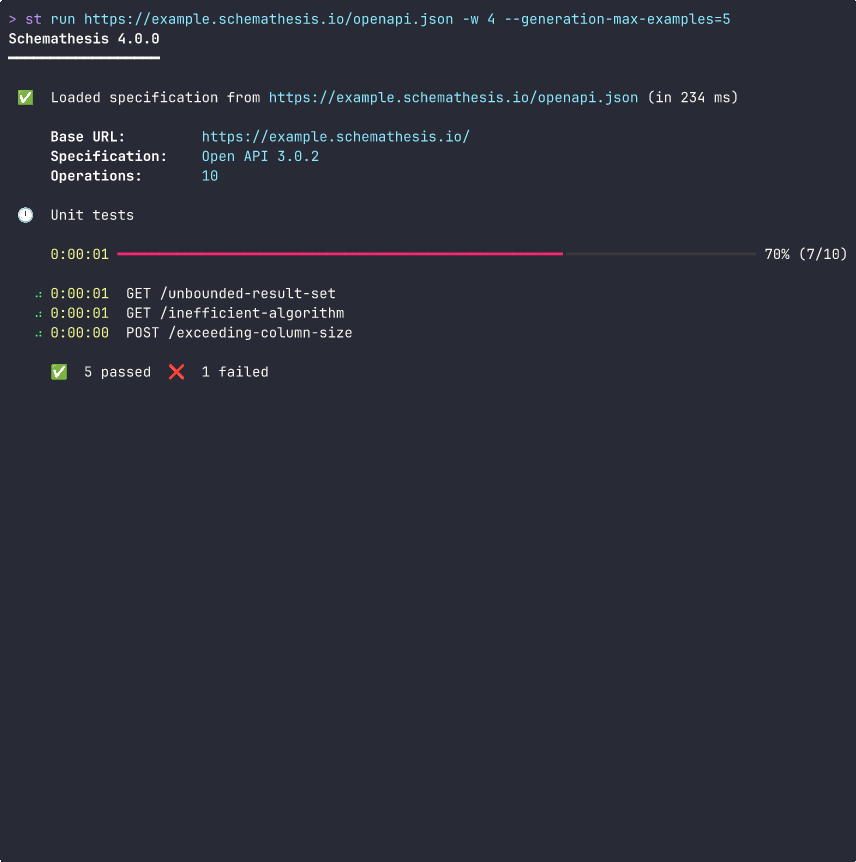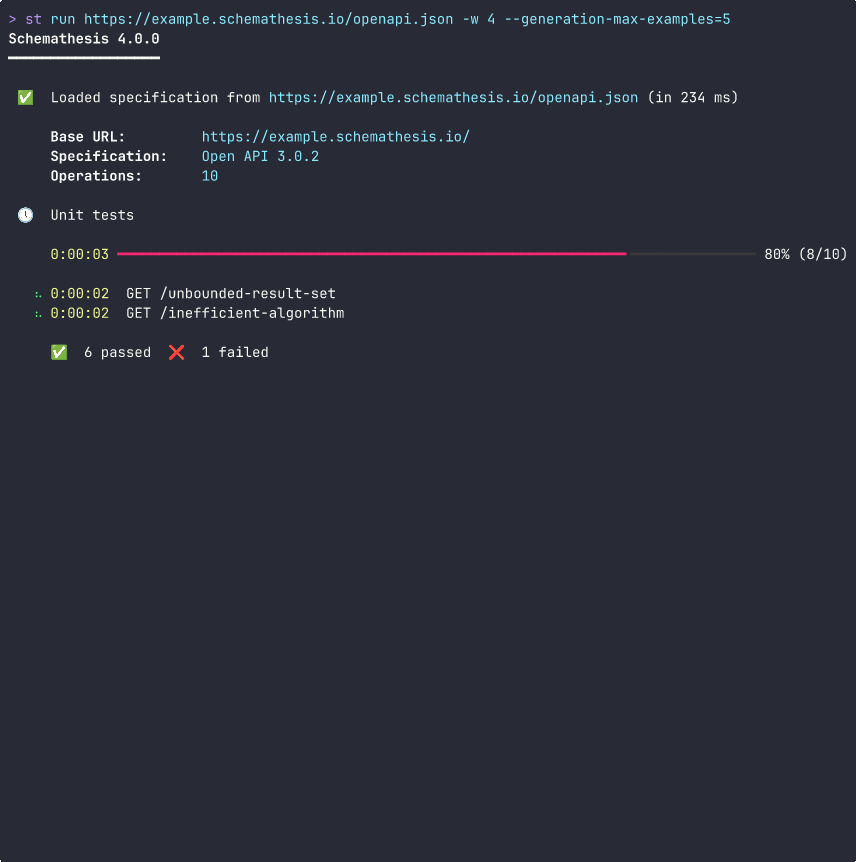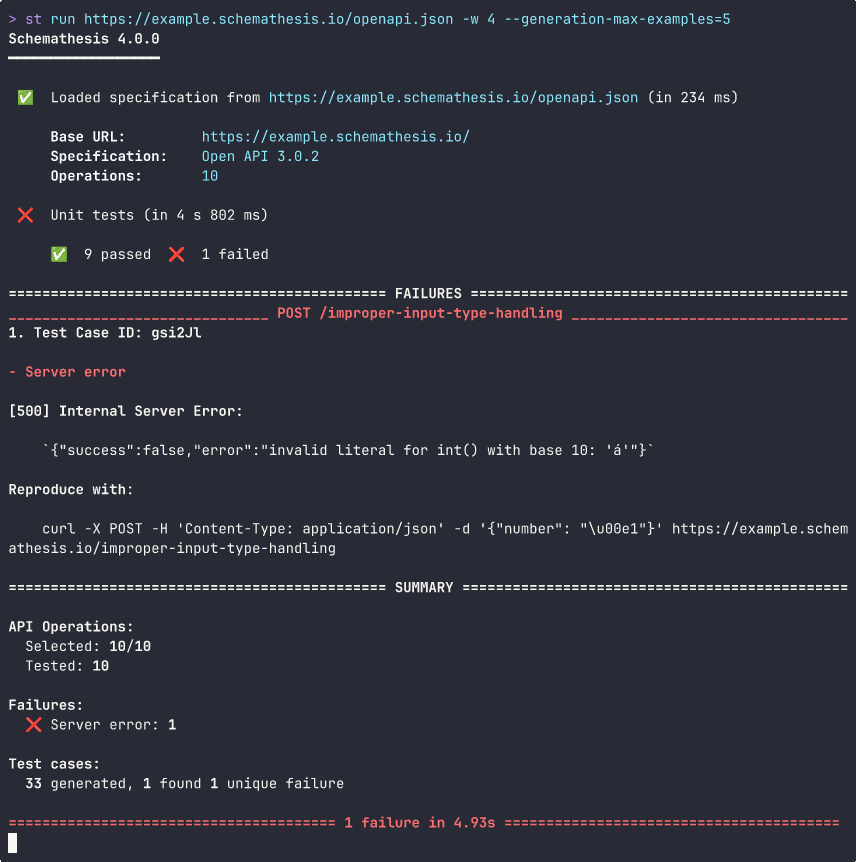
Schemathesis automatically finding a server error
Finding bugs that manual testing missed

Try it now

# Test a demo API - finds real bugs in 30 seconds
uvx schemathesis run https://example.schemathesis.io/openapi.json

# Test your own API
uvx schemathesis run https://your-api.com/openapi.json

What problems does it solve?

  • ๐Ÿ’ฅ 500 errors that crash your API on edge case inputs
  • ๐Ÿ“‹ Schema violations where your API returns different data than documented
  • ๐Ÿšช Validation bypasses where invalid data gets accepted
  • ๐Ÿ”— Integration failures when responses don't match client expectations
  • ๐Ÿ”„ Stateful bugs where operations work individually but fail in realistic workflows

What can it do?

  • โš™๏ธ Config file - auth, phases, and per-operation overrides in schemathesis.toml. No Python.
  • ๐Ÿ” Authentication - static headers, Basic, per-security-scheme credentials, or custom refresh logic.
  • ๐Ÿ”— Stateful testing - operation links inferred from your schema, no manual wiring.
  • ๐Ÿง  Adaptive testing - learns constraints, ids, and auth from responses, reusing them mid-run.
  • โœ… Custom checks - assert your own business rules next to the built-in ones.
  • ๐Ÿ“– Fuzz dictionaries - mix real ids, wordlists, or LLM-generated payloads into generated data.
  • ๐ŸŒ Rate limiting - cap the request rate, or use auto to follow Retry-After on 429.
  • ๐Ÿ“Š Reports - JUnit, VCR, HAR, NDJSON, JSON, and Allure.
  • ๐ŸŽฏ Schema coverage - keyword-level coverage report showing which constraints your tests exercised.
  • ๐Ÿ” Replay & baseline - re-run past failures and fail CI only on new ones.

โš ๏ธ Upgrading from older versions? Check our Migration Guide for key changes.

Installation & Usage

Command Line:

uv tool install schemathesis
schemathesis run https://your-api.com/openapi.json

Config file (schemathesis.toml, no Python needed):

headers = { Authorization = "Bearer ${API_TOKEN}" }
generation.max-examples = 500
rate-limit = "auto"

Python Tests:

import schemathesis

schema = schemathesis.openapi.from_url("https://your-api.com/openapi.json")


@schema.parametrize()
def test_api(case):
    # Tests with random data, edge cases, and invalid inputs
    case.call_and_validate()


# Stateful testing: Tests workflows like: create user -> get user -> delete user
APIWorkflow = schema.as_state_machine()
# Creates a test class for pytest/unittest
TestAPI = APIWorkflow.TestCase

CI/CD:

- uses: schemathesis/action@v3
  with:
    schema: "https://your-api.com/openapi.json"

Who uses it

Used by teams at Spotify, WordPress, JetBrains, and Red Hat.

"Schemathesis is the best tool for fuzz testing of REST APIs on the market. We at Red Hat use it for examining our applications in functional and integration testing levels." - Dmitry Misharov, RedHat

See it in action

๐Ÿ”ฌ Live Benchmarks showing continuous testing results from real-world APIs:

  • Code & API schema coverage achieved
  • Issues found with detailed categorization
  • Performance across different fuzzing strategies

Documentation

๐Ÿ“š Documentation with guides, examples, and API reference. Start here:

  • Quick Start - 5 minutes
  • CLI Tutorial - 20 minutes
  • Pytest Tutorial - 15 minutes

Get Help

  • ๐Ÿ’ฌ Discord community
  • ๐Ÿ› GitHub issues

Contributing

We welcome contributions! See our contributing guidelines and join discussions in issues or Discord.

Acknowledgements

Schemathesis is built on top of Hypothesis, a powerful property-based testing library for Python.

License

This project is licensed under the terms of the MIT license.

Press Escape to close the search panel.

Donate

Buy me a Coffee

Penetration Testing Services

penetration Testing Services

Web Application Security Quiz

Web Application Security Quiz

Daily Bug Bounty Writeups - Twitter

Daily Bug Bounty Writeups

Download our Latest Android Application

Guide for Penetration Testing

Daily Bug Bounty Writeups - Telegram

Daily Bug Bounty Writeups

Author

Piyush
Senior Product Security Engineer

Ethical Hacker || Penetration Tester || Gamer || Blogger || Product Security Engineer || AI Security

READ ARTICLE

Donate

Buy me a Coffee

Recent Posts

  • AI-Generated Code Security Bugs: A Vibe Coding Case Study
    AI-Generated Code Security Bugs: A Vibe Coding Case Study
    October 7, 2026/
    0 Comments
  • Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    September 8, 2026/
    0 Comments
  • DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    August 27, 2026/
    0 Comments

Follow Us

SecurityCipher

Practical security guides, vulnerability deep-dives, and hands-on resources for bug bounty hunters and penetration testers.

Useful Links

  • Security Checklists
  • Cybersecurity Jobs
  • Blogs
  • About
  • Contact
ยฉ 2026 Security Cipher. All rights reserved. Privacy Policy ยท Terms & Conditions