

WARNING: Axiom Classic is now in maintenance mode. We encourage you to transition to the new Ax Framework. In the coming months, we will introduce essential quality-of-life updates to Axiom Classic before 2025. Long live Axiom!
Axiom is a dynamic infrastructure framework to efficiently work with multi-cloud environments, build and deploy repeatable infrastructure focused on offensive and defensive security.
Axiom works by pre-installing your tools of choice onto a 'base image', and then using that image to deploy fresh instances. From there, you can connect and instantly gain access to many tools useful for both bug hunters and pentesters. With the power of immutable infrastructure, most of which is done for you, you can just spin up 15 boxes, perform a distributed nmap/ffuf/screenshotting scan, and then shut them down.
Because you can create many disposable instances very easily, axiom allows you to distribute scans of many different tools (full list here). Once installed and setup, you can distribute a scan of a large set of targets across 100-150 instances within minutes and get results extremely quickly. This is called axiom-scan.
Axiom supports several cloud providers, eventually, axiom should be completely cloud agnostic allowing unified control of a wide variety of different cloud environments with ease. Currently, DigitalOcean, IBM Cloud, Linode, Azure and AWS are officially supported providers. GCP isnt supported but is partially implemented and on the roadmap. If you would like prioritization of a feature or provider implementation, please contact me @pry0cc on Twitter and we can discuss :)
- Introduction
- Troubleshooting & FAQ
- Quickstart
- Demo
- Story
- Installation Instructions
- Scan Modules
- Installed Packages
- Contributors
The original and best supported provider for Axiom is Digital Ocean! If you're signing up for a new Digital Ocean account, please use my link for $100 free credit!

The best supported business provider for Axiom is IBM Cloud! If you're signing up for a new IBM Cloud account, please use this link for $200 free credit!


This will create a docker container, initiate axiom-configure and axiom-build and then drop you out of the docker container. Once the Packer image is successfully created, you will likely need to re-exec into your docker container via docker exec -it $container_id zsh.
docker exec -it $(docker run -d -it --platform linux/amd64 ubuntu:20.04) sh -c "apt update && apt install git -y && git clone https://github.com/pry0cc/axiom ~/.axiom/ && cd && .axiom/interact/axiom-configure"
You should use an OS that supports our easy install.
For Linux systems you will also need to install the newest versions of all packages beforehand sudo apt dist-upgrade.
bash <(curl -s https://raw.githubusercontent.com/pry0cc/axiom/master/interact/axiom-configure)
If you have any problems with this installer, or if using an unsupported OS please refer to Installation.
In this demo (sped up out of respect for your time ;) ), we show how easy it is to initialize and ssh into a new instance.
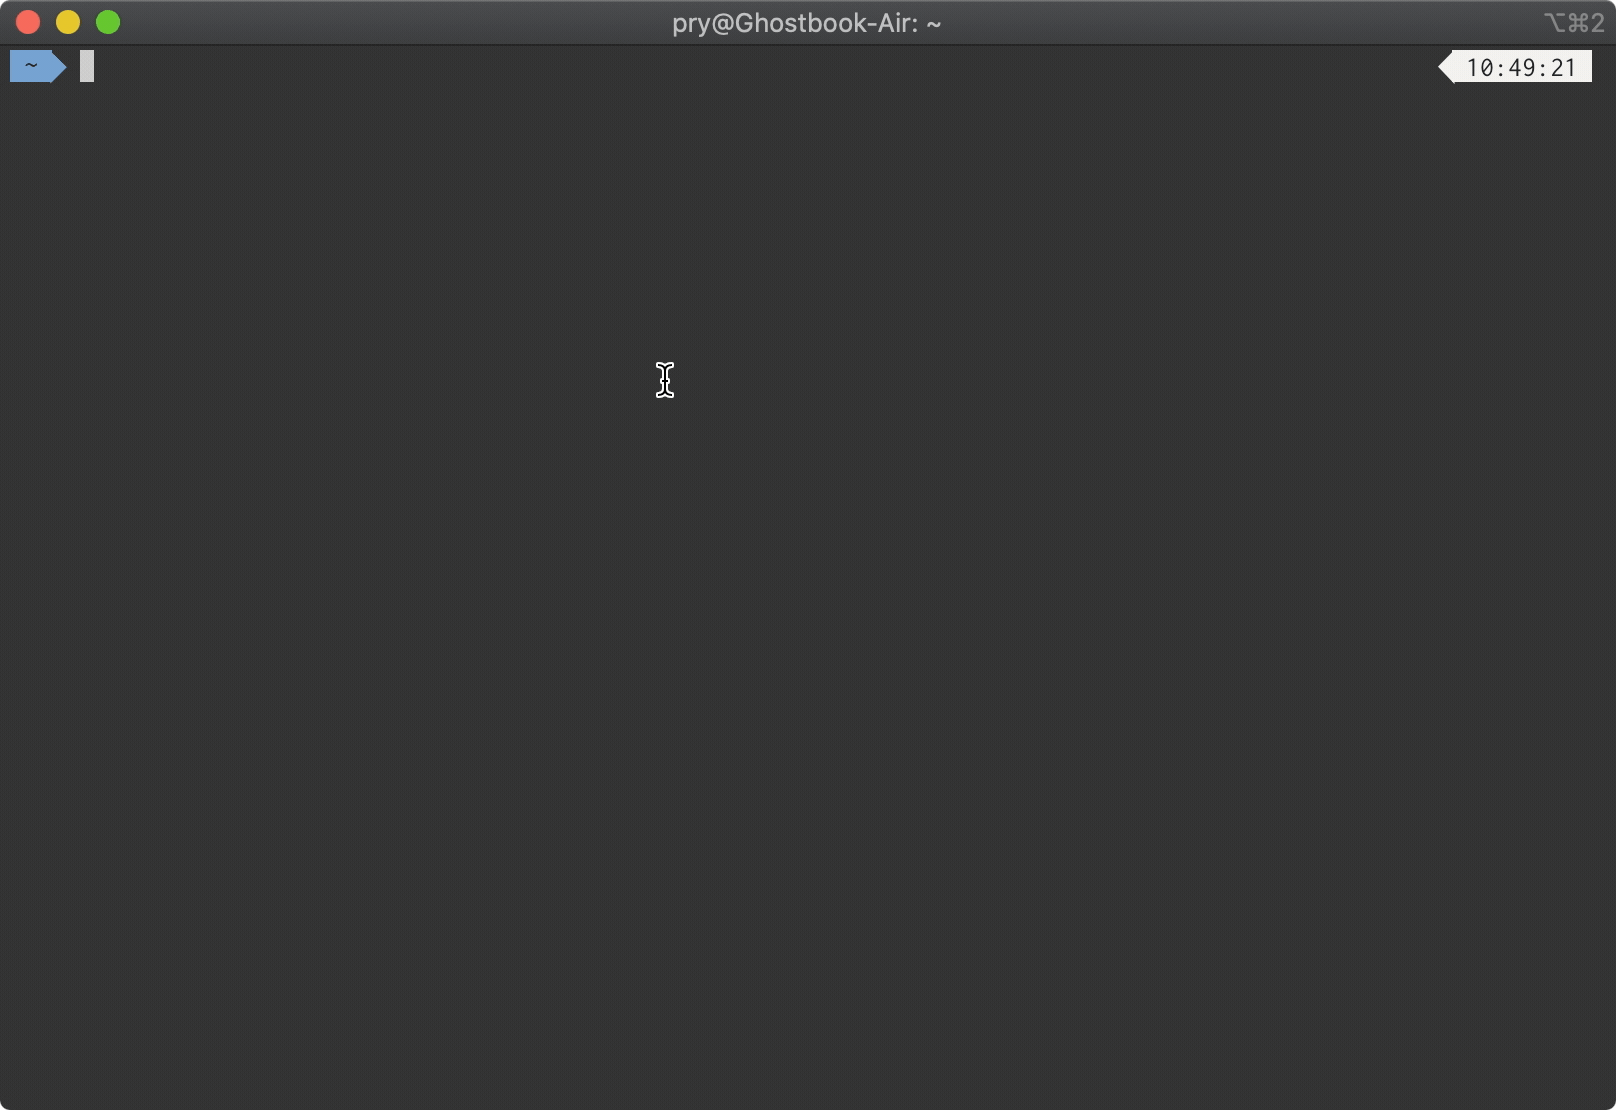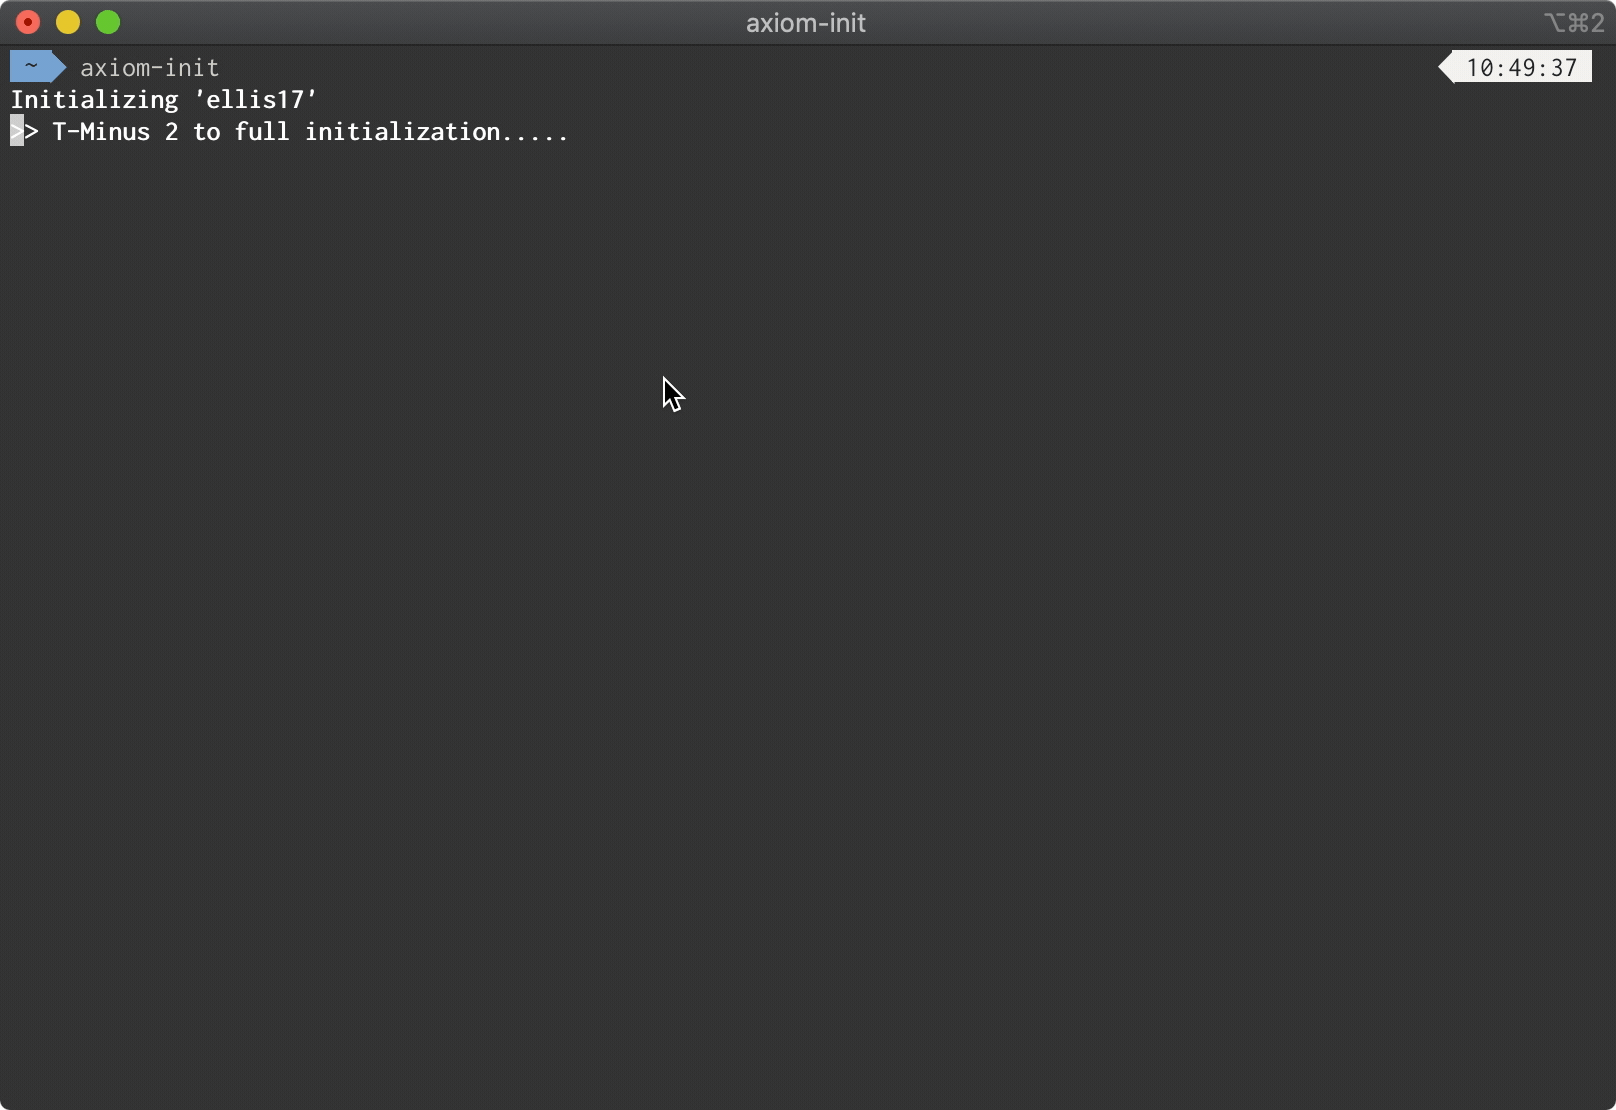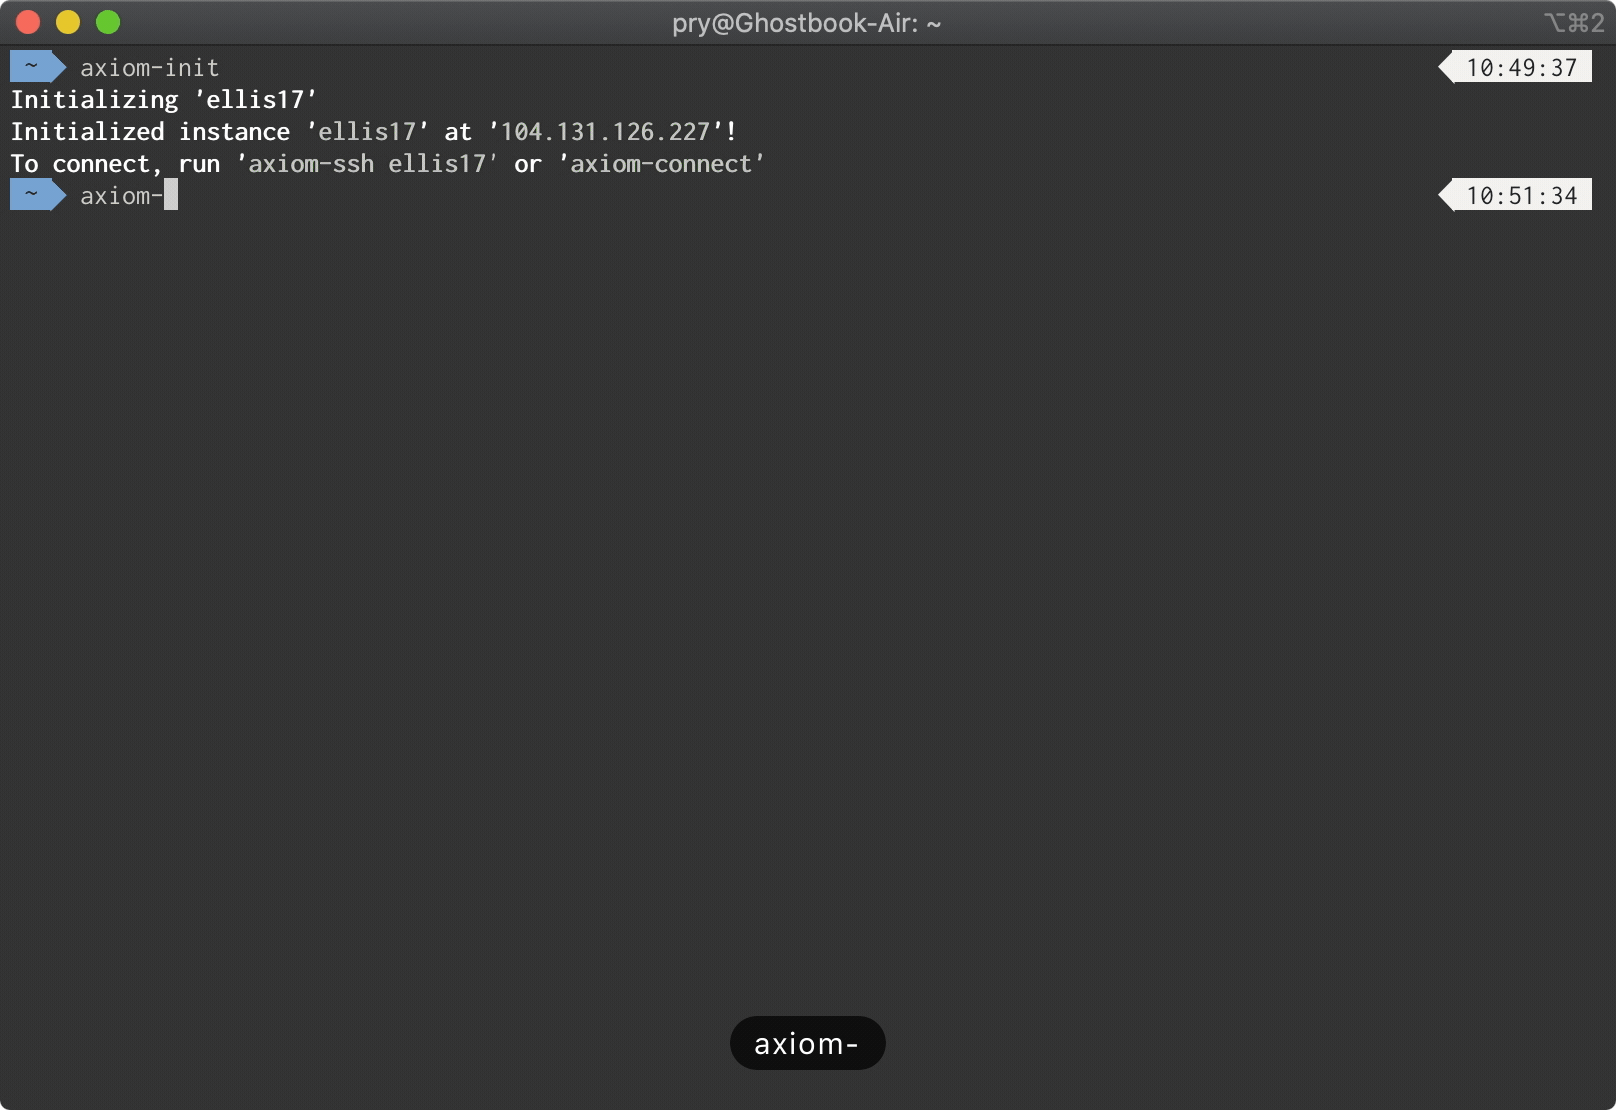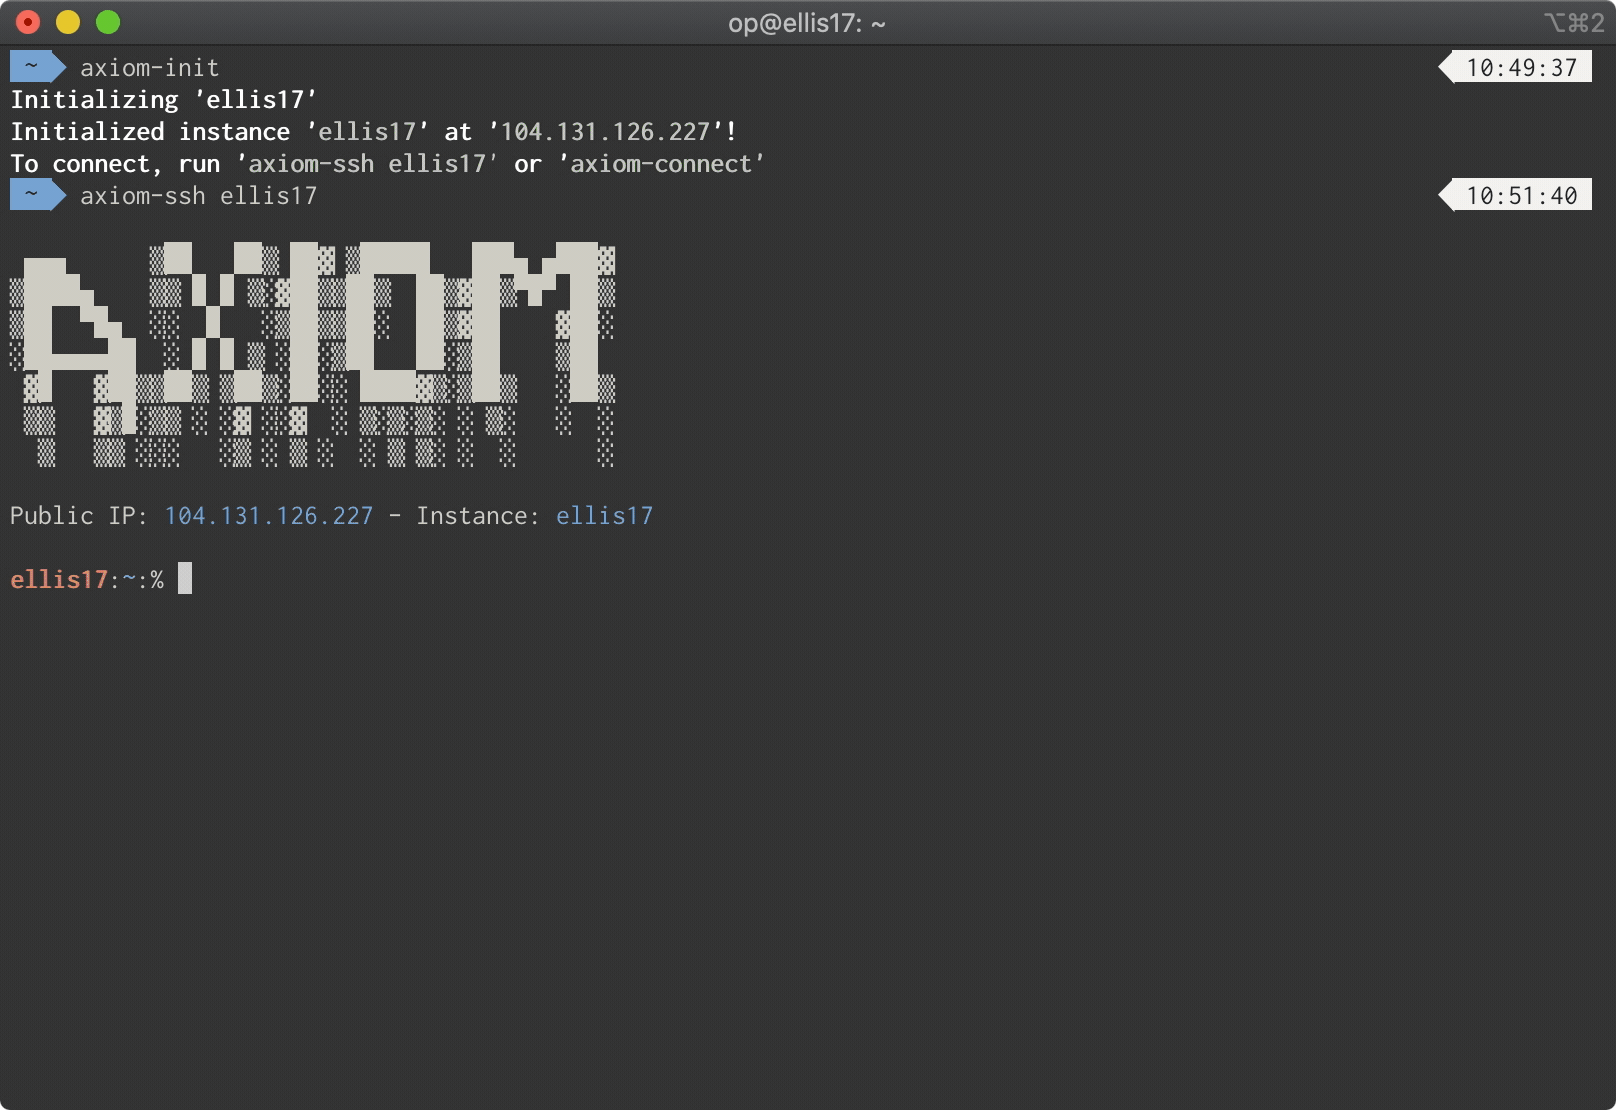

If you like Axiom and it saves you time, money or just brings you happy feelings, please show your support through sponsorship! Click the little sponsor button in the header and sponsor for as little as $1 per month :)
Or buy me a coffee to keep me powered :)
| OS | Supported | Easy Install | Tested |
|---|---|---|---|
| Ubuntu | Yes | Yes | Ubuntu 20.04 |
| Kali | Yes | Yes | Kali 2021.3 |
| Debian | Yes | Yes | Debian 10 |
| Windows | Yes | Yes | WSL w/ Ubuntu |
| MacOS | Yes | Yes | MacOS 11.6 |
| Arch Linux | Yes | No | Yes |
We've had some really fantastic additions to axiom, great feedback through issues, and perseverence through our heavy beta phase!
A list of all contributors can be found here, thank you all!
The original logo was made by our amazing s0md3v! Thank you for making axiom look sleek as hell! Really beats my homegrown logo :)

The awesome referral banners were inspired by fleex and were made by the one and only xm1k3!
for default provisioner
- [x] aiodnsbrute
- [x] Amass
- [x] anew
- [x] anti-burl
- [x] aquatone
- [x] Arjun
- [x] assetfinder
- [x] axiom
- [x] axiom-dockerfiles
- [x] cent
- [x] cero
- [x] chaos-client
- [x] commix
- [x] concurl
- [x] Corsy
- [x] CrackMapExec
- [x] crlfuzz
- [x] dalfox
- [x] dirdar
- [x] DNSCewl
- [x] dnsgen
- [x] dnsrecon
- [x] dns resolvers by trickest
- [x] dnsvalidator
- [x] dnsx
- [x] Docker
- [x] ERLPopper
- [x] exclude-cdn
- [x] feroxbuster
- [x] fff
- [x] ffuf
- [x] findomain
- [x] gau
- [x] gauplus
- [x] getJS
- [x] gf
- [x] Gf-Patterns
- [x] github-endpoints
- [x] github-subdomains
- [x] Go
- [x] gobuster
- [x] google-chrome
- [x] gorgo
- [x] gospider
- [x] gowitness
- [x] gron
- [x] Gxss
- [x] hakrawler
- [x] hakrevdns
- [x] httprobe
- [x] httpx
- [x] interactsh-client
- [x] Interlace
- [x] ipcdn
- [x] jaeles
- [x] kiterunner
- [x] kxss
- [x] leaky-paths
- [x] LinkFinder
- [x] masscan
- [x] massdns
- [x] medusa
- [x] meg
- [x] naabu
- [x] nmap
- [x] nuclei
- [x] OpenRedireX
- [x] ParamSpider
- [x] phantomjs
- [x] proxychains-ng
- [x] puredns
- [x] qsreplace
- [x] responder.py
- [x] RustScan
- [x] s3scanner
- [x] scrying
- [x] SecLists
- [x] shuffledns
- [x] six2dez dns permutations
- [x] sqlmap
- [x] subfinder
- [x] subjack
- [x] subjs
- [x] testssl
- [x] thc-hydra
- [x] tlsx
- [x] trufflehog
- [x] ufw
- [x] unimap
- [x] wafw00f
- [x] waybackurls
- [x] webscreenshot
- [x] wpscan
for default provisioner
- [x] bison
- [x] build-essential
- [x] fail2ban
- [x] firebird-dev
- [x] flex
- [x] git
- [x] grc
- [x] jq
- [x] libgcrypt11-dev_1.5.4-3+really1.8.1-4ubuntu1.2_amd64.deb
- [x] libgcrypt20-dev
- [x] libgpg-error-dev
- [x] libgtk2.0-dev
- [x] libidn11-dev
- [x] libmemcached-dev
- [x] libmysqlclient-dev
- [x] libpcap-dev
- [x] libpcre3-dev
- [x] libpq-dev
- [x] libssh-dev
- [x] libssl-dev
- [x] libsvn-dev
- [x] net-tools
- [x] ohmyzsh
- [x] p7zip
- [x] python3-pip
- [x] ruby-dev
- [x] rubygems
- [x] ufw
- [x] unzip
- [x] zsh
- [x] zsh-autosuggestions
- [x] zsh-syntax-highlighting
 Do you want to add a package to axiom? Read the wiki!