SecurityCipher
Home Blog About Us

Learn Paths, courses, and reference docs

  • ๐Ÿš€ Start Here Beginner path through the site
  • ๐Ÿ—บ๏ธ Penetration Testing Roadmap Structured path to become a pentester
  • ๐ŸŽ“ Free Security Courses Current free Udemy coupon listings
  • ๐Ÿ“„ Secure Code Explain Vulnerable vs secure code side by side
  • ๐ŸŽฏ Penetration Testing Tricks Field notes for real engagements
  • ๐Ÿ“– Vulnerability Explain How common vulns actually work

Checklists Interactive reviews and LLM risks

  • โœ… Security Checklists Hub All interactive security checklists
  • ๐Ÿ“‹ Writeup Checklists Steps derived from real writeups
  • ๐Ÿง  LLM AI Security Checklist Controls for LLM apps
  • ๐Ÿค– OWASP LLM Top 10 LLM Top 10 risks mapped out
  • ๐Ÿงฐ Burp Suite Guide Step-by-step Burp tutorials
  • ๐Ÿ“˜ Payload Field Manual Safe-first probes and signals

Practice Browser labs, games, and explorers

  • ๐Ÿ”ฌ Interactive Labs SQL injection, AI, architecture review
  • ๐ŸŽฎ Security Games Phishing, JWT, WAF, and more
  • ๐Ÿš— On-Call Drive Neon-city arcade security missions
  • โ€ข Shift Zero SOC desk: phish, OTP, malware, tickets
  • โ“ Application Security Quiz Web, secure coding, and cloud quizzes
  • ๐Ÿ—บ๏ธ OWASP Top 10 Explorer Clickable risk map with signals
  • ๐Ÿ”€ Interactive Attack Paths Recon-to-impact chains

Tools & Career Databases, jobs, and community

  • ๐Ÿ› ๏ธ Security Tools Curated recon, SAST, and bounty tools
  • ๐Ÿ”Ž CVE Lookup Multi-source CVE intelligence
  • ๐Ÿ’ฐ Bug Bounty Programs Live public scopes to search
  • ๐Ÿ’ผ Cybersecurity Jobs Roles from company career pages
  • ๐Ÿง‘โ€๐Ÿ’ป Security Researchers Community profiles and submissions
  • ๐ŸŽค Security Conferences Upcoming and past events
Browse all Security resources hub Freelance Security โ†’
My Resume
Freelance SecurityFreelance
New Security Researchers Join the directory - submit your profile for review Submit profile โ†’
← Security Tools View on GitHub

OpenRedireX

A Fuzzer for OpenRedirect issues

OpenRedireX

A fuzzer for detecting open redirect vulnerabilities

๐Ÿ—๏ธ Install โ›๏ธ Usage ๐Ÿ“š Dependencies

OpenRedirex

Install

git clone https://github.com/devanshbatham/openredirex
cd openredirex
sudo chmod +x setup.sh
./setup.sh

Usage

The script is executed from the command line and has the following usage options:

openredirex [-p payloads] [-k keyword] [-c concurrency]
  • -p, --payloads: File containing a list of payloads. If not specified, a hardcoded list is used.
  • -k, --keyword: Keyword in URLs to replace with payload. Default is "FUZZ".
  • -c, --concurrency: Number of concurrent tasks. Default is 100.

The script expects a list of URLs as input. Each URL should contain the keyword specified by the -k option. The script replaces the keyword with each of the payloads, and attempts to fetch the modified URL.

Example usage:

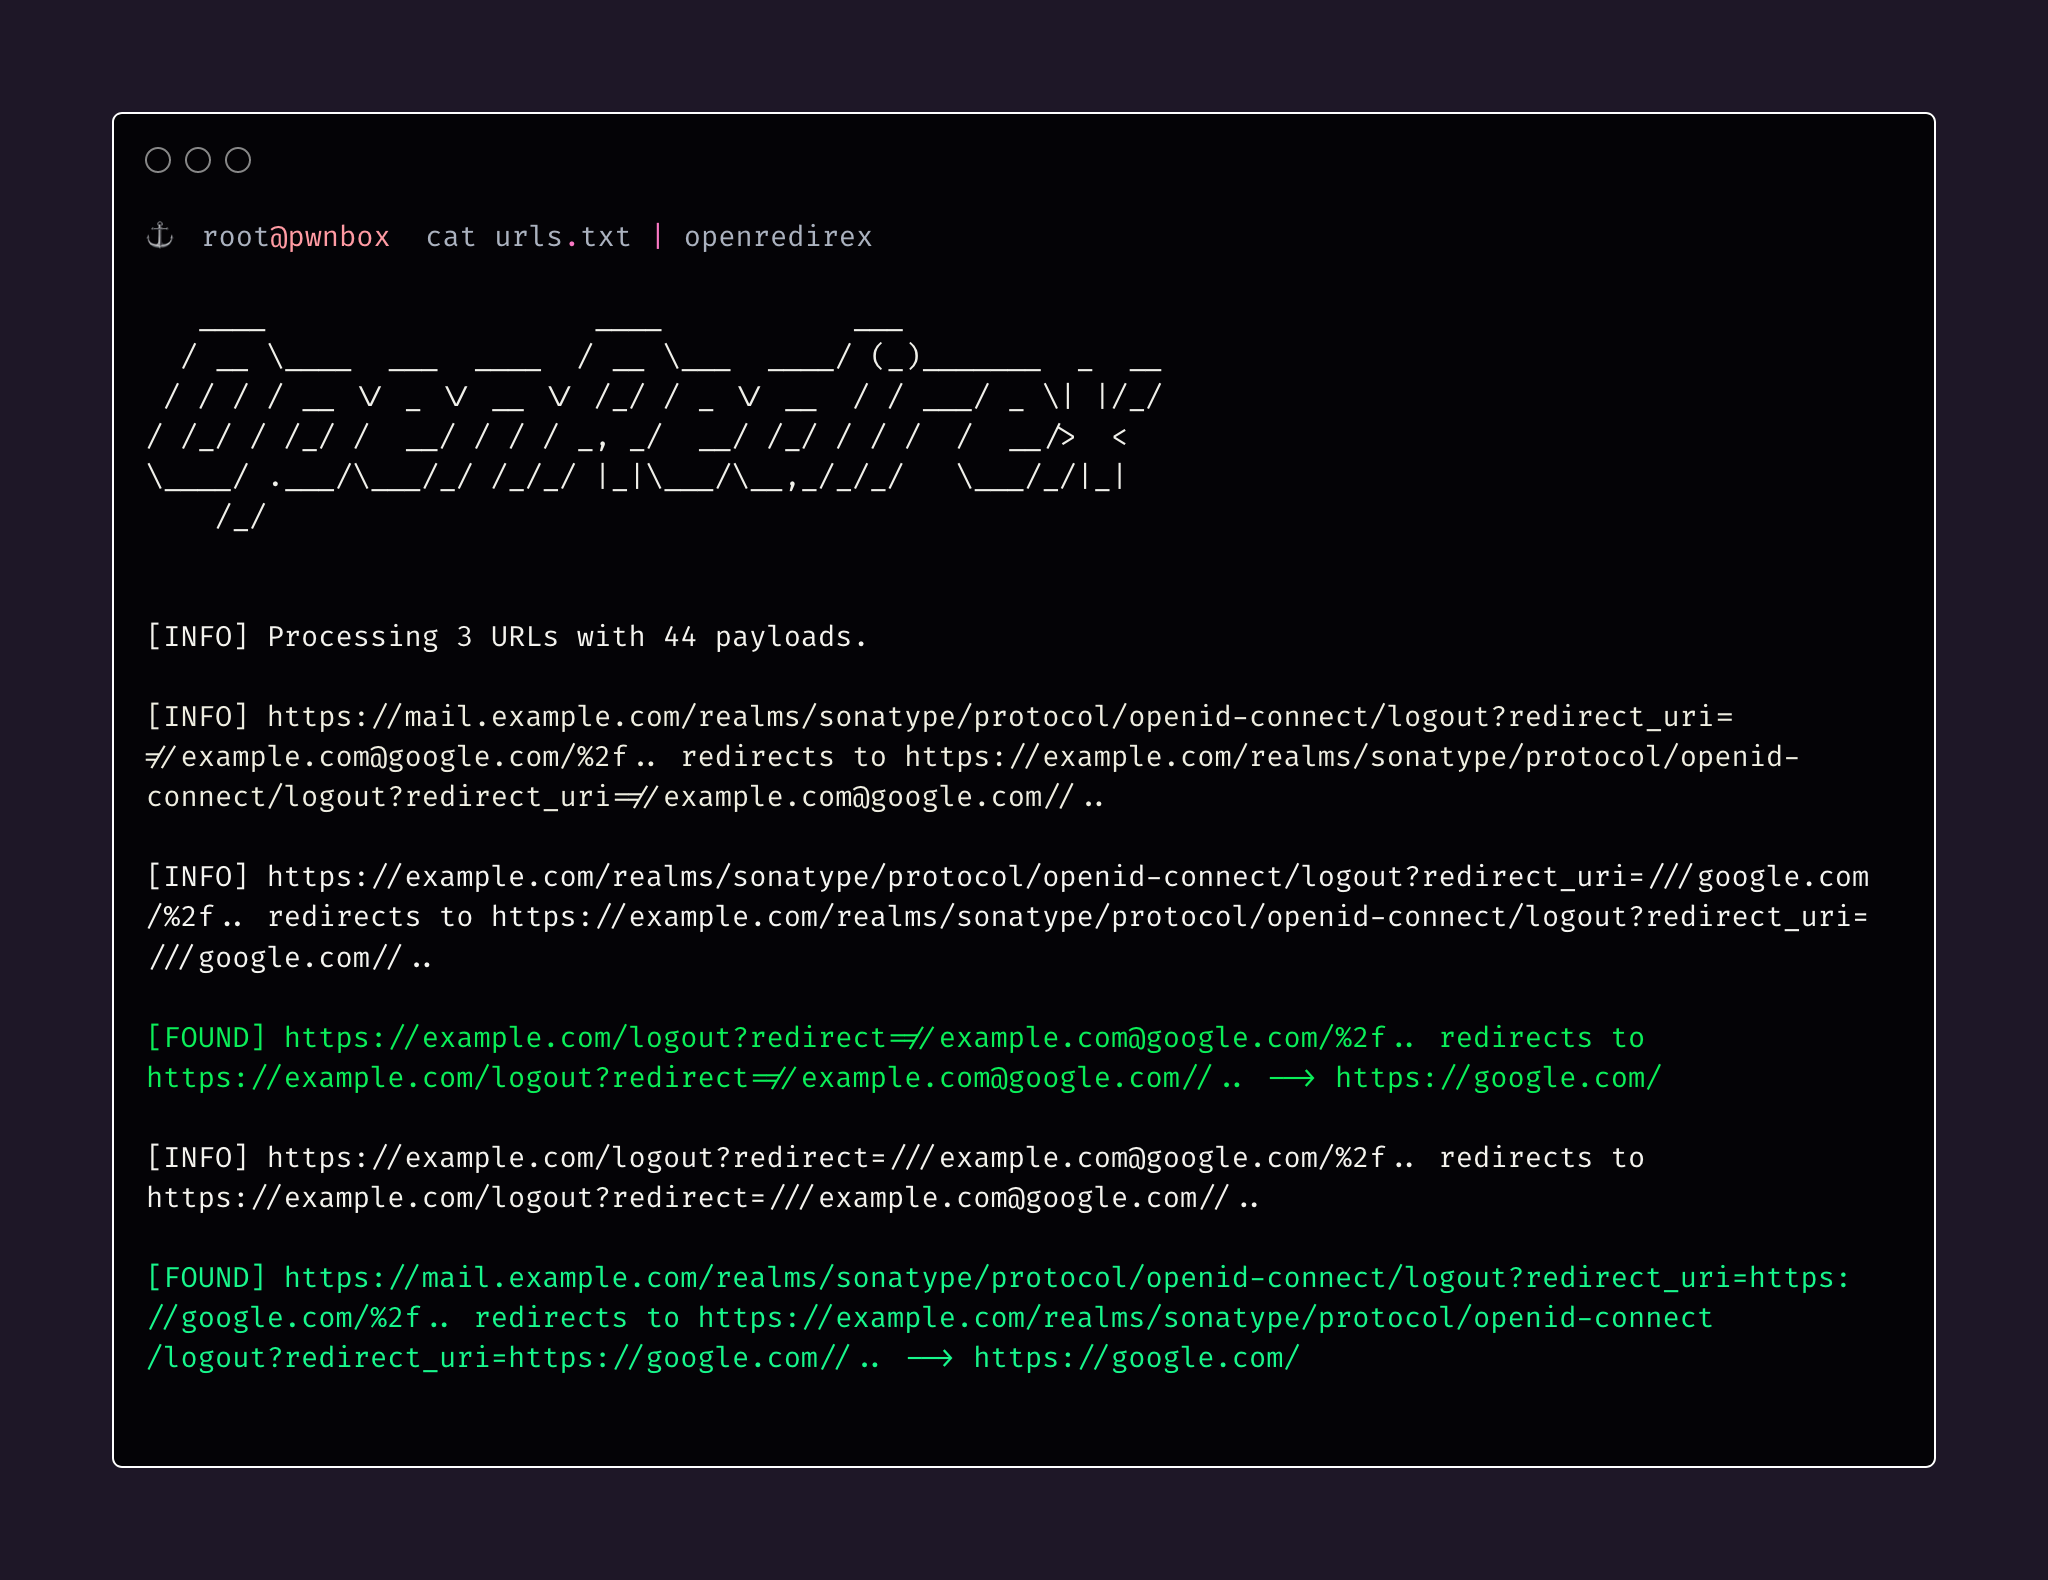
cat list_of_urls.txt |  openredirex -p payloads.txt -k "FUZZ" -c 50

List of URLs should look like below:

cat list_of_urls.txt

https://newsroom.example.com/logout?redirect=FUZZ
https://auth.example.com/auth/realms/sonatype/protocol/openid-connect/logout?redirect_uri=test
https://exmaple.com/php?test=baz&foo=bar

This example reads URLs from the file list_of_urls.txt, replaces all the values of the parameters to FUZZ (if --keyword is not supplied), then again replaces the keyword FUZZ or the supplied keyword with each payload from payloads.txt, and fetches each URL concurrently, with a maximum of 50 concurrent tasks.

Dependencies

The script uses the following libraries:

  • argparse for handling command-line arguments.
  • aiohttp for making HTTP requests.
  • tqdm for displaying progress.
  • concurrent.futures for handling concurrent tasks.
  • asyncio for managing asynchronous tasks.

You need to install these dependencies before running the script. Most of them are part of the standard Python library. You can install aiohttp and tqdm using pip:

pip install aiohttp tqdm

You can use this script to check for open redirects in web applications. However, you should only use it on systems that you have been given explicit permission to test.

Press Escape to close the search panel.

Donate

Buy me a Coffee

Penetration Testing Services

penetration Testing Services

Web Application Security Quiz

Web Application Security Quiz

Daily Bug Bounty Writeups - Twitter

Daily Bug Bounty Writeups

Download our Latest Android Application

Guide for Penetration Testing

Daily Bug Bounty Writeups - Telegram

Daily Bug Bounty Writeups

Author

Piyush
Senior Product Security Engineer

Ethical Hacker || Penetration Tester || Gamer || Blogger || Product Security Engineer || AI Security

READ ARTICLE

Donate

Buy me a Coffee

Recent Posts

  • OpenSSH Password Bypass on Alpine (CVE-2026-123158)
    OpenSSH Password Bypass on Alpine (CVE-2026-123158)
    November 5, 2026/
    0 Comments
  • The $6.3 Billion Binance Hack: A Product Security Breakdown of What Happened, What Should Have Happened, and What Changes Now
    The $6.3 Billion Binance Hack: A Product Security Breakdown of What Happened, What Should Have Happened, and What Changes Now
    November 5, 2026/
    0 Comments
  • October 2026 Patch Audit: PHP2Shell, GitLab, Node, LiteLLM
    October 2026 Patch Audit: PHP2Shell, GitLab, Node, LiteLLM
    October 26, 2026/
    0 Comments

Follow Us

SECURITY DISPATCH

Subscribe to SecurityCipher

Get the latest bug bounty writeups, offensive security tooling, and zero-day analyses delivered to your inbox.

Subscription Form

SecurityCipher

Practical security guides, vulnerability deep-dives, and hands-on resources for bug bounty hunters and penetration testers.

Useful Links

  • Security Checklists
  • Cybersecurity Jobs
  • Blogs
  • Docs
  • About
  • Contact

Free Resources

  • Linux Commands
  • Security Mindmaps
  • Career Roadmaps
  • Certifications
  • Interview Questions
  • Wordlist Strategy
  • Browser Privacy Check
  • ISO 27001 SoA Lite
  • India DPDP Checklist
ยฉ 2026 Security Cipher. All rights reserved. Privacy Policy ยท Terms & Conditions ยท DMCA ยท
PRIVACY & COOKIES

Hi there! We value your privacy

We use cookies to improve your browsing experience on our website, to analyze our website traffic, and to understand where our visitors are coming from. Would you like to go ahead with the cookies?

To modify your preferences afterwards, click on the Privacy Policy or footer link.

Security Researchers
OPEN DIRECTORY Verified Network

Are you a security researcher or bug hunter?

Join our open directory of verified pentesters, showcase your achievements, and get recognized!

Submit Researcher Profile โ†’