SecurityCipher
Home Blog About Us
Resources β–Ό
βœ… Security Checklists Hub πŸ—ΊοΈ Penetration Testing Roadmap πŸ€– OWASP Top 10 for LLM Applications 🧠 LLM AI Security Checklist πŸ› οΈ Security Tools 🎯 Penetration Testing Tricks πŸ“„ Secure Code Explain πŸ“– Vulnerability Explain ☁️ AWS Cloud Security Checklist
My Resume
Our ServicesServices
New On-Call Drive Drive the neon city, jack in, and clear security tickets Play now β†’
← Security Tools View on GitHub

ParamSpider

Mining parameters from dark corners of Web Archives.

paramspider

Mining URLs from dark corners of Web Archives for bug hunting/fuzzing/further probing

πŸ“– About β€’ πŸ—οΈ Installation β€’ ⛏️ Usage β€’ πŸš€ Examples β€’ 🀝 Contributing β€’

paramspider

About

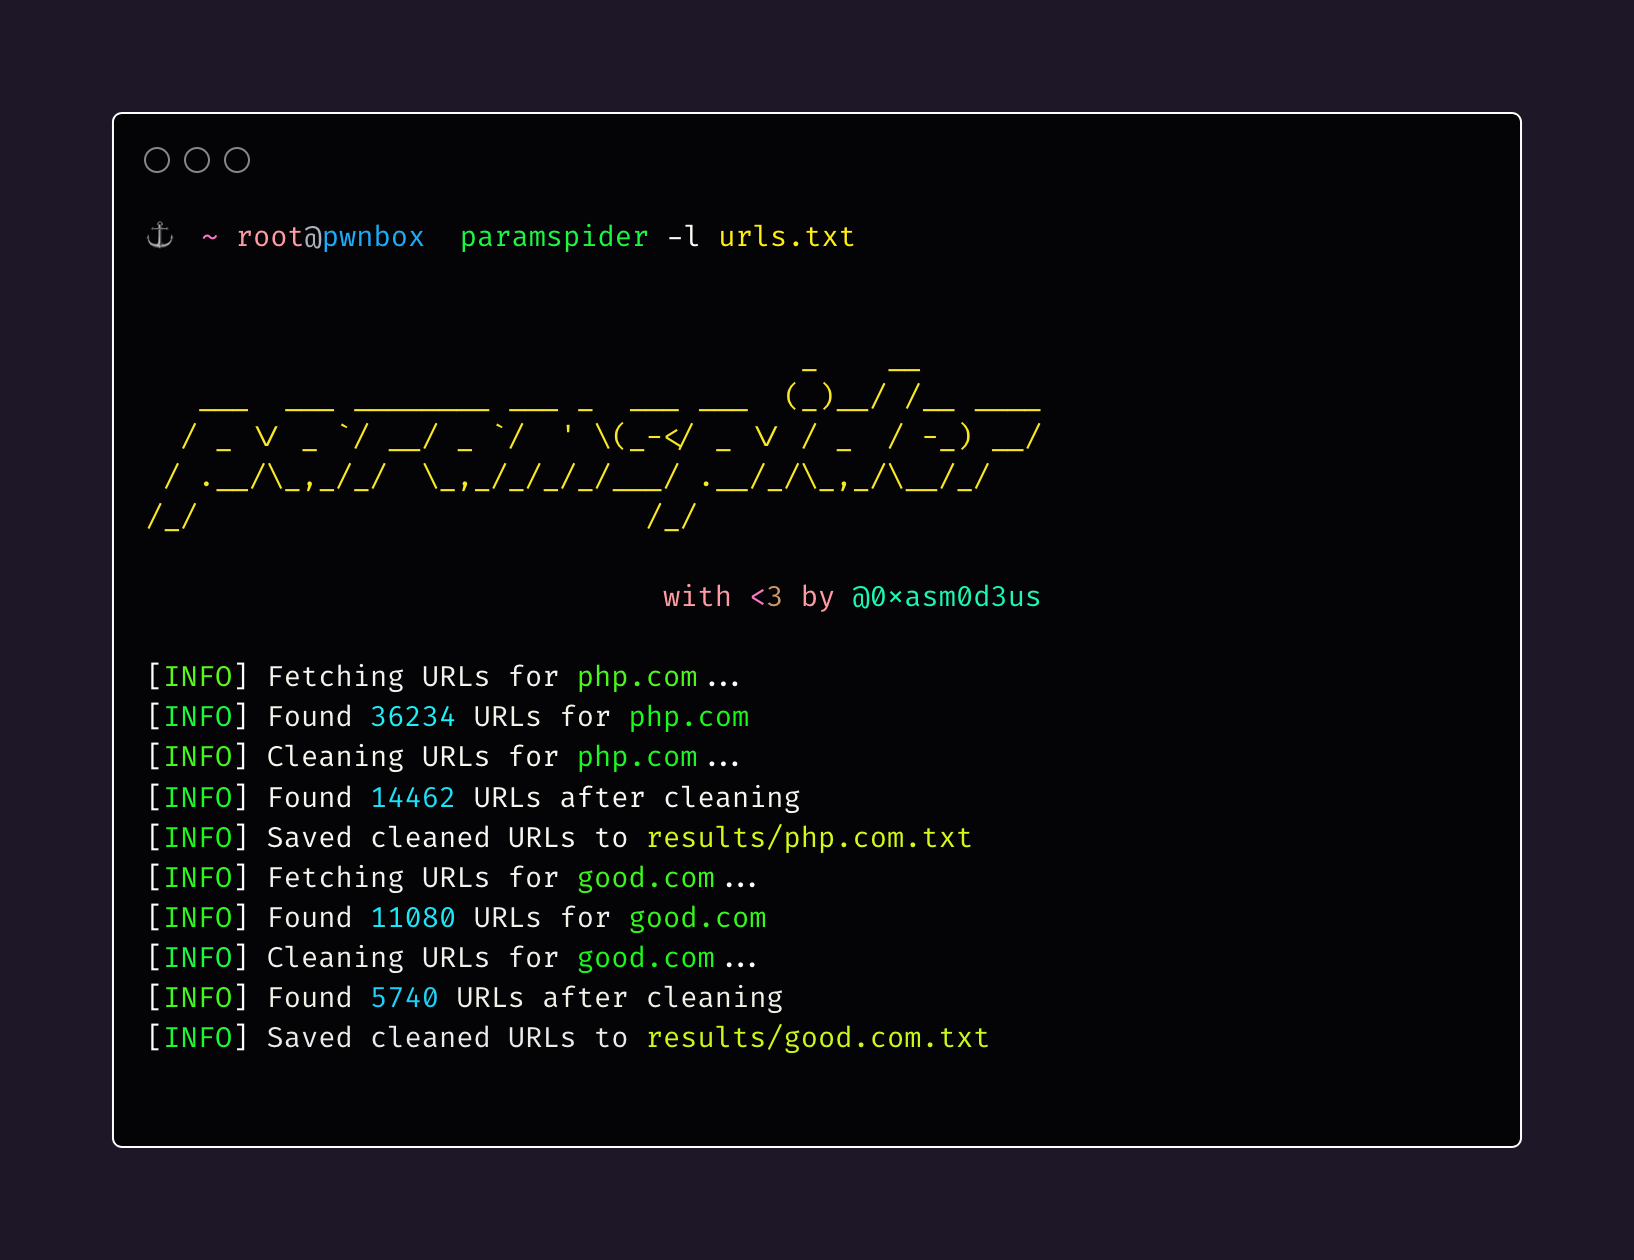
paramspider allows you to fetch URLs related to any domain or a list of domains from Wayback achives. It filters out "boring" URLs, allowing you to focus on the ones that matter the most.

Installation

To install paramspider, follow these steps:

git clone https://github.com/devanshbatham/paramspider
cd paramspider
pip install .

Usage

To use paramspider, follow these steps:

paramspider -d example.com

Examples

Here are a few examples of how to use paramspider:

  • Discover URLs for a single domain:

    paramspider -d example.com
  • Discover URLs for multiple domains from a file:

    paramspider -l domains.txt
  • Stream URLs on the termial:

    paramspider -d example.com -s
  • Set up web request proxy:

    paramspider -d example.com --proxy '127.0.0.1:7890'
  • Adding a placeholder for URL parameter values (default: "FUZZ"):

     paramspider -d example.com -p '"><h1>reflection</h1>'

Star History

Star History Chart

Penetration Testing Services

penetration Testing Services

Web Application Security Quiz

Web Application Security Quiz

Daily Bug Bounty Writeups - Twitter

Daily Bug Bounty Writeups

Download our Latest Android Application

Guide for Penetration Testing

Daily Bug Bounty Writeups - Telegram

Daily Bug Bounty Writeups

Author

Piyush
Senior Product Security Engineer

Ethical Hacker || Penetration Tester || Gamer || Blogger || Product Security Engineer || AI Security

READ ARTICLE

Donate

Buy me a Coffee

Recent Posts

  • Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    Cloud Misconfig Bounty Hunting in 2026: Open Buckets, Firebase, and Secrets
    September 8, 2026/
    0 Comments
  • DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    DevSecOps From Laptop to Production: A Practical Security Pipeline Guide
    August 27, 2026/
    0 Comments
  • The CVE Flood Is a Lie: How to Hunt When AI Dumps 36% More Bugs But Exploitation Only Grows 10%
    The CVE Flood Is a Lie: How to Hunt When AI Dumps 36% More Bugs But Exploitation Only Grows 10%
    August 25, 2026/
    0 Comments

Follow Us

SecurityCipher

Practical security guides, vulnerability deep-dives, and hands-on resources for bug bounty hunters and penetration testers.

Useful Links

  • Security Checklists
  • Cybersecurity Jobs
  • Blogs
  • About
  • Contact
Β© 2026 SecurityCipher. All rights reserved. Privacy Policies Β· Terms & Conditions